BACK TO DIRECTORY
Beplus Security Headers & Script Auditor gives WordPress site owners three things in one screen:
- Security header toggles — enable X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Strict-Transport-Security, Permissions-Policy, Content-Security-Policy (with an optional report-only mode), and the legacy X-XSS-Protection header, each with sensible defaults.
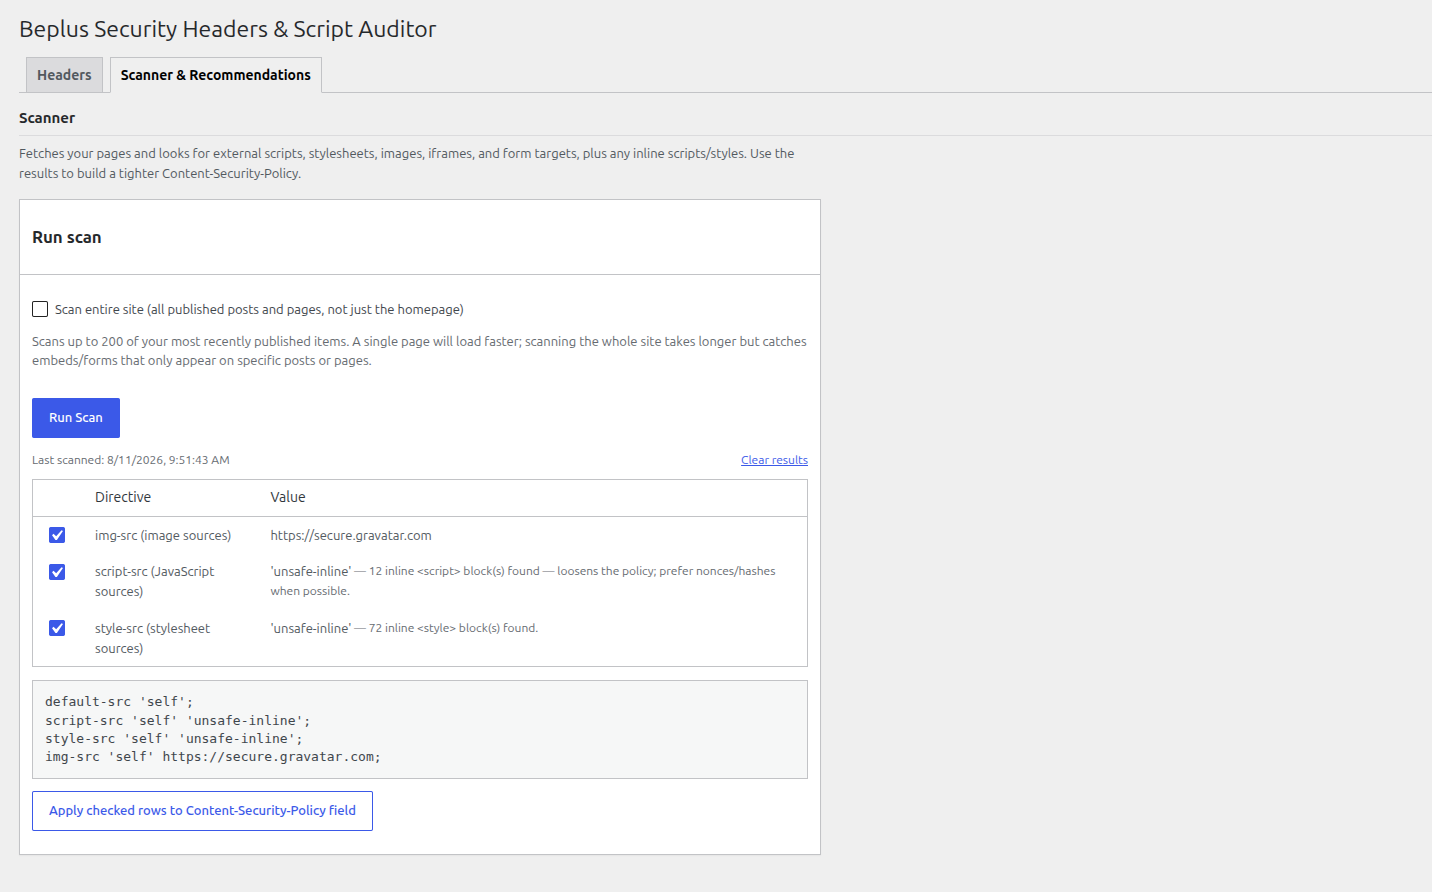
- A scanner — fetches your homepage, or optionally your whole site (up to 200 of your most recently published posts/pages), and lists every external script, stylesheet, image, iframe, and form target it finds, plus a count of inline scripts/styles.
- Recommendations you control — every finding is listed as a checkbox row; uncheck anything you don’t want, and the Content-Security-Policy preview updates live. Apply the checked rows to the CSP field with one click, review it, then press Save. Nothing is ever sent automatically.
There’s also a repeatable table for adding any other custom response header your site needs.
Why use this plugin
- No external service calls, tracking, or phone-home behaviour — the scan only requests pages on your own site.
- Every setting is sanitized on save, and header values are stripped of line breaks to prevent HTTP header injection.
- Sensible, conservative defaults: only X-Frame-Options, X-Content-Type-Options, and Referrer-Policy are enabled out of the box. HSTS, Permissions-Policy, CSP, and X-XSS-Protection are opt-in since they can affect how your site behaves and should be reviewed first.
Screenshots
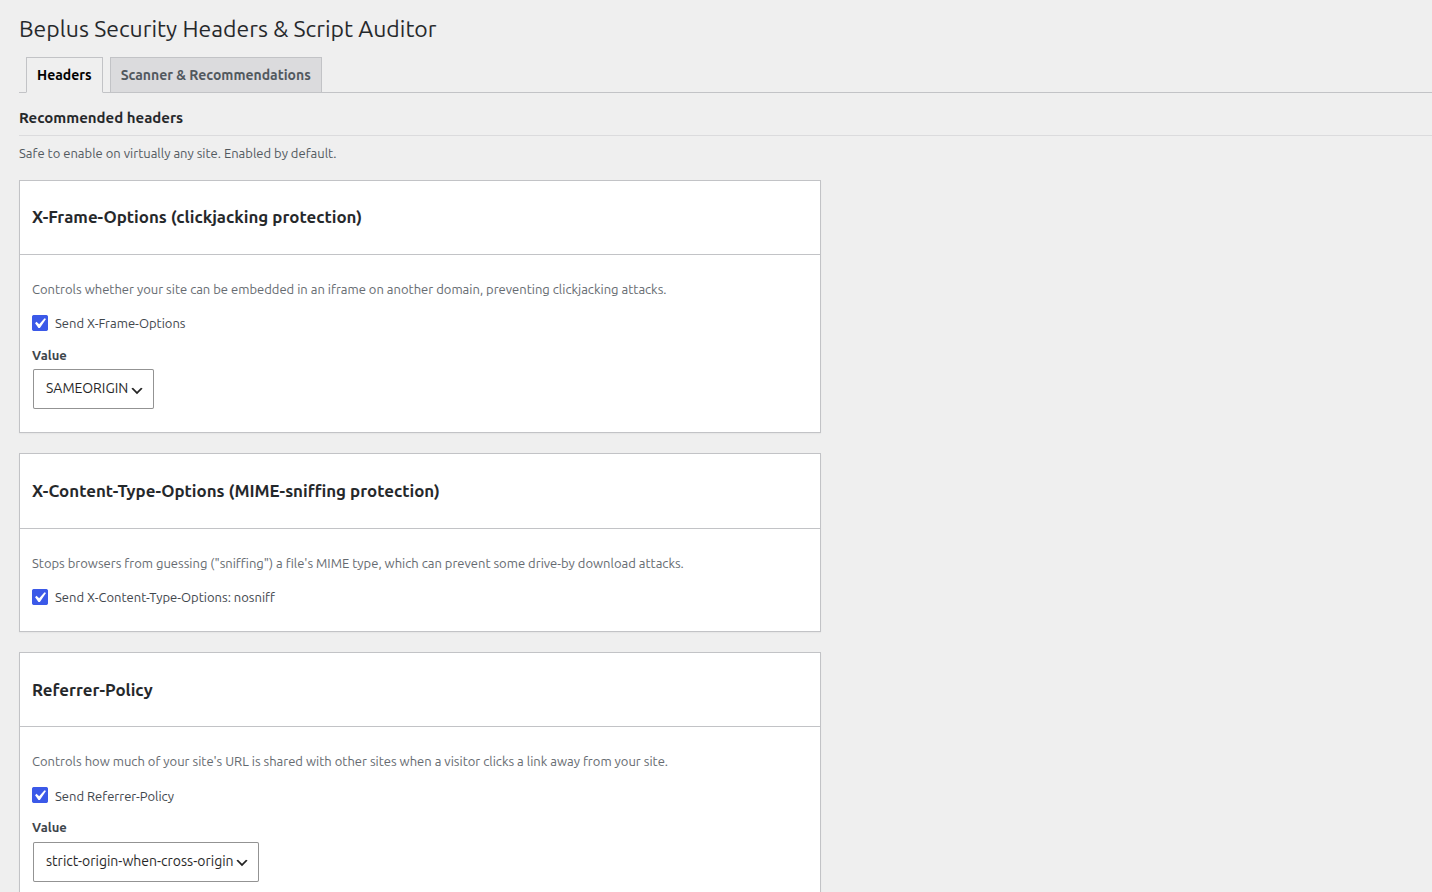
The Headers tab, where each security header can be toggled and configured.
The Scanner tab, showing detected external resources as a checklist and a live Content-Security-Policy preview.
Plugin Details
Active Installs
0Total Downloads
143Version
1.0.1Requires WP
6.0Requires PHP
7.4Tested Up To
7.1Added
2026-08-19Last Updated
2026-09-13 10:29am GMTRatings
5
0
4
0
3
0
2
0
1
0