
WordPress relies mostly on name-based validation when deciding whether or not to allow a particular file, leaving the door open for various kinds of attacks.
Lord of the Files adds to this content-based validation and sanitizing, making sure that files are what they say they are and safe for inclusion on your site.
The main features include:
- Robust real filetype detection;
- Full MIME alias mapping;
- SVG sanitization (if SVG uploads have been independently allowed);
- File upload validation debugger;
- Fixes issues related to #40175 that have been present since WordPress
4.7.1. - Fixes ambiguous media extensions #40921
Requirements
- WordPress 5.2 or later.
- PHP 7.4 or later.
domPHP extension.fileinfoPHP extension.mbstringPHP extension.xmlPHP extension.
Please note: it is not safe to run WordPress atop a version of PHP that has reached its End of Life. Future releases of this plugin might, out of necessity, drop support for old, unmaintained versions of PHP. To ensure you continue to receive plugin updates, bug fixes, and new features, just make sure PHP is kept up-to-date. 🙂
Privacy Policy
This plugin does not make use of or collect any “Personal Data”.
Screenshots
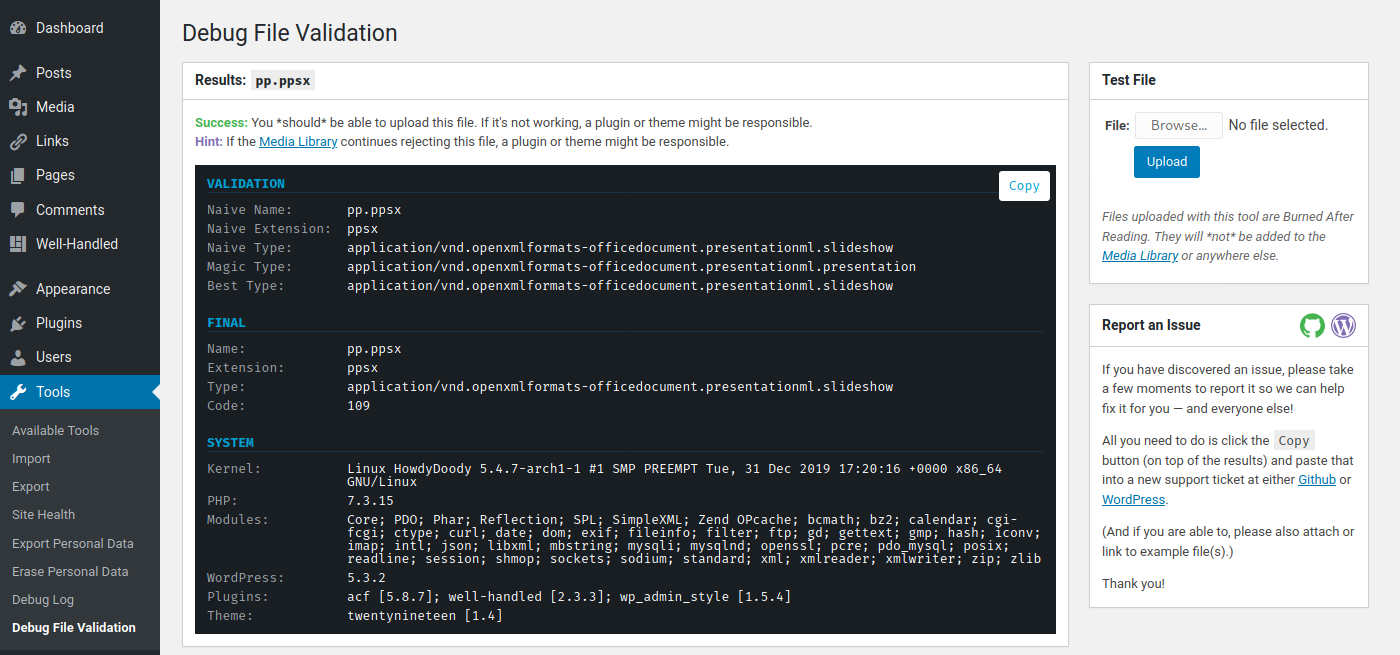
Example output from Tools > Debug File Validation.
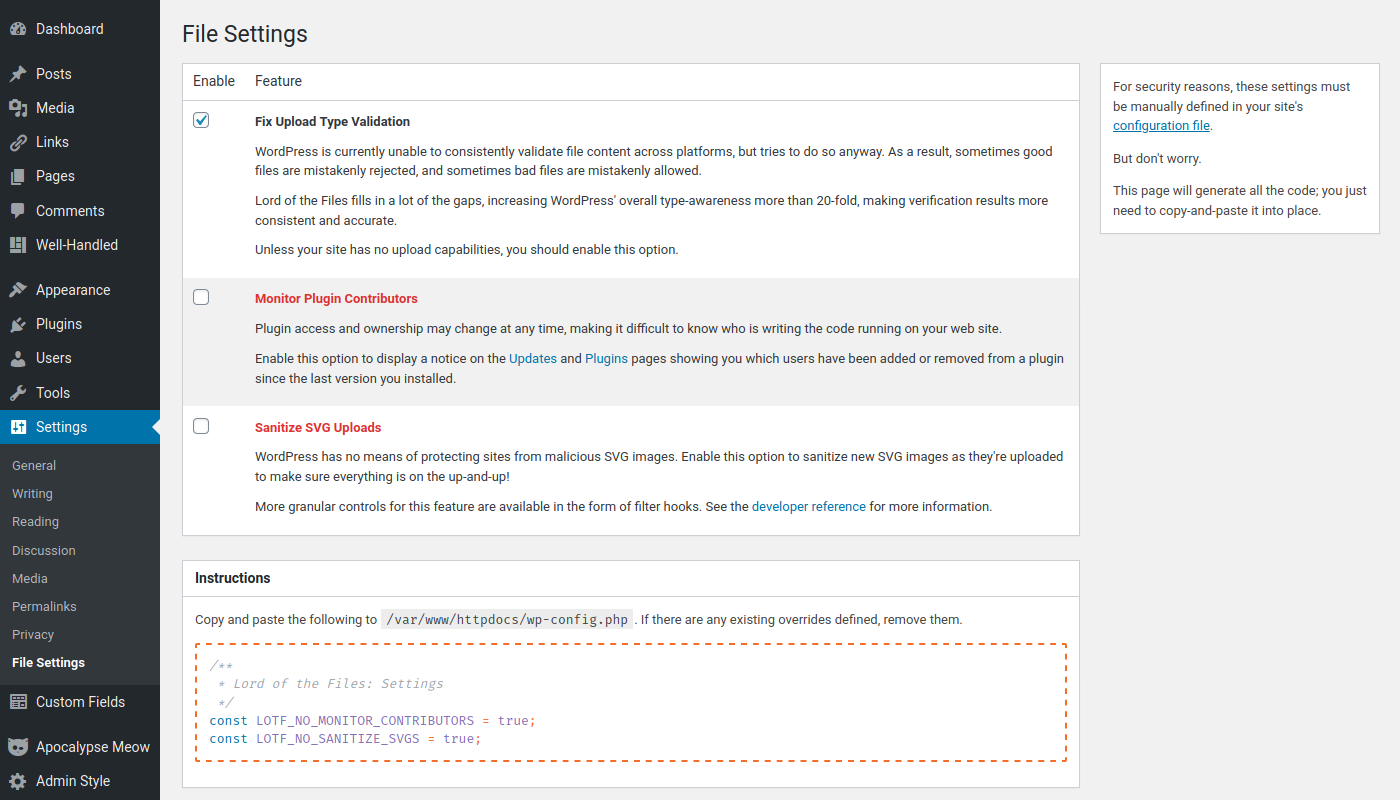
The plugin includes a settings wizard under Settings > File Settings.