Unlike basic JWT plugins that use single long-lived tokens, JWT Auth Pro implements modern OAuth 2.0 security best practices with short-lived access tokens and secure refresh tokens.
Why JWT Auth Pro?
The Problem with Basic JWT Plugins:
* Long-lived tokens (24h+) = Higher security risk
* No refresh mechanism = Tokens live until expiry
* XSS vulnerable = Tokens stored in localStorage
* No revocation = Can’t invalidate compromised tokens
JWT Auth Pro Solution:
* Short-lived access tokens (1h default) = Minimal attack window
* Secure refresh tokens = HTTP-only cookies, XSS protected
* Automatic token rotation = Fresh tokens on each refresh
* Complete session control = Revoke any user session instantly
Features
- Simple JWT Authentication – Clean, stateless token-based auth
- HTTPOnly Refresh Tokens – Secure refresh tokens in HTTP-only cookies
- Token Rotation – Automatic refresh token rotation for enhanced security
- CORS Support – Proper cross-origin request handling
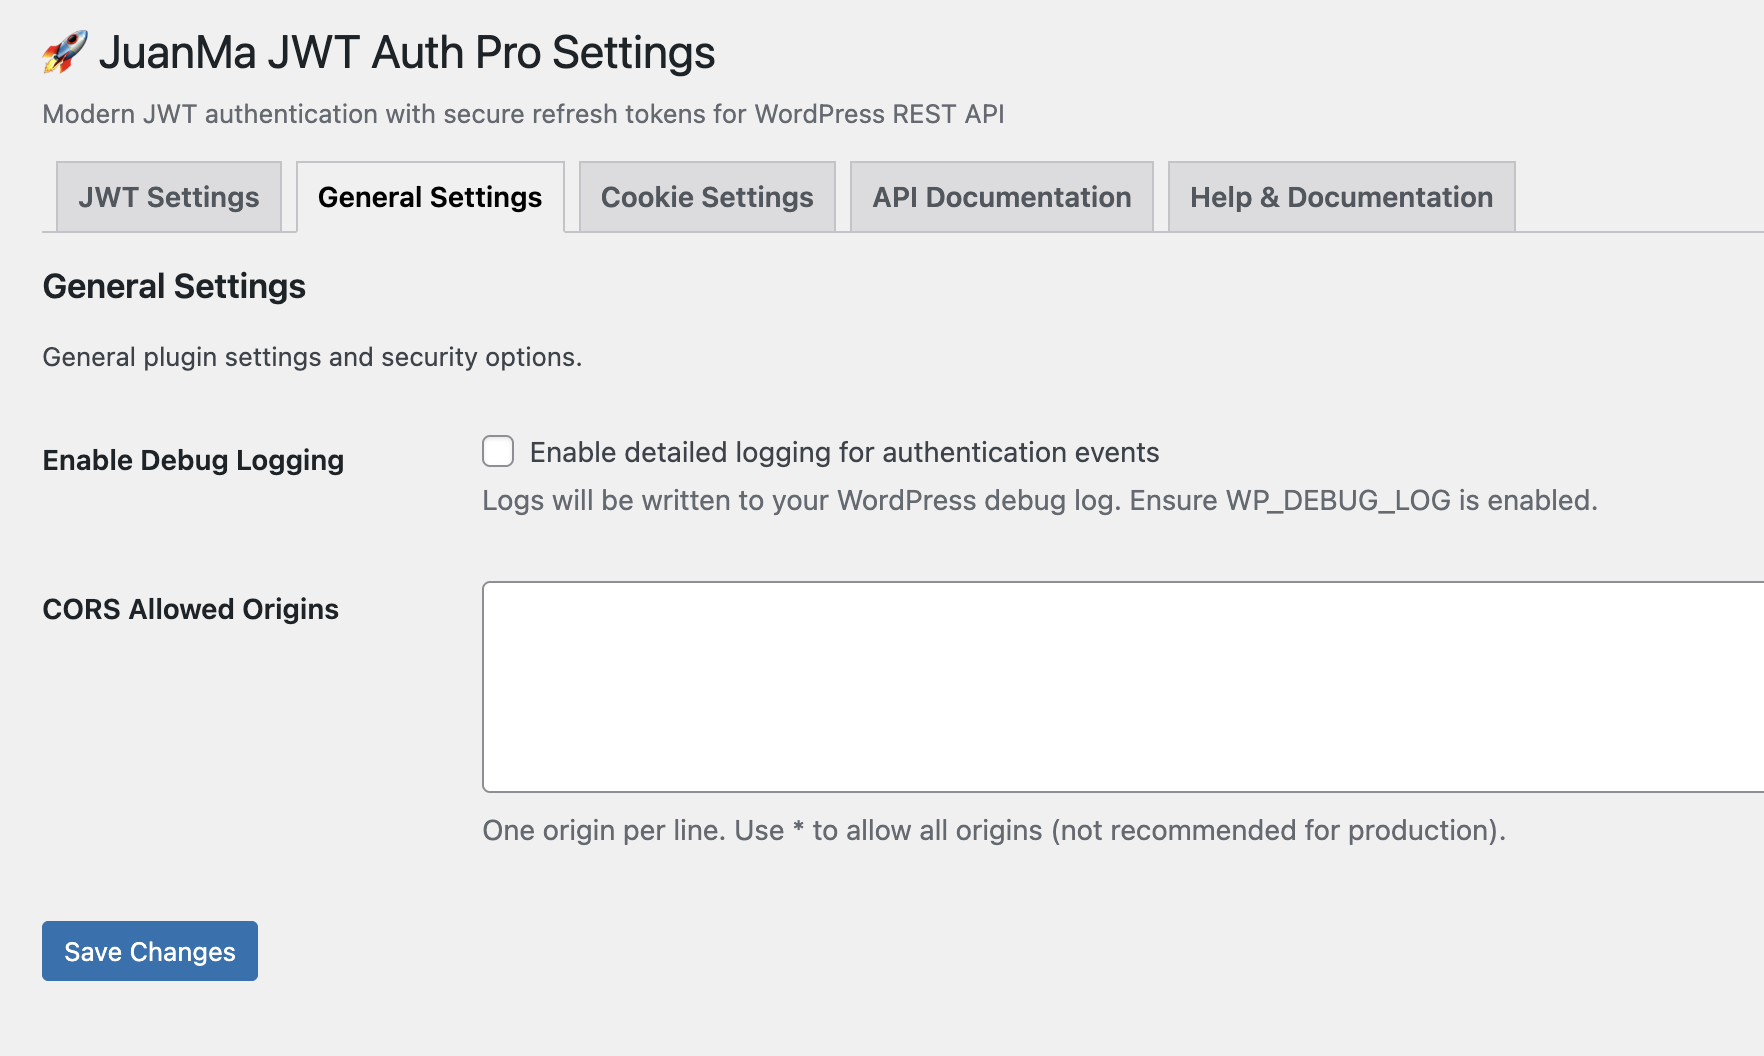
- Clean Admin Interface – Simple configuration in WordPress admin
- Developer Friendly – Clear endpoints and documentation
Security Comparison
Feature
Basic JWT Plugins
JWT Auth Pro
Token Lifetime
Long (hours/days)
Short (1 hour)
Refresh Tokens
None
Secure HTTP-only
XSS Protection
Limited
HTTP-only cookies
Token Revocation
Manual only
Automatic rotation
Session Management
None
Database tracking
Security Metadata
None
IP + User Agent
Perfect for:
- Single Page Applications (React, Vue, Angular)
- Mobile Applications (iOS, Android)
- API Integrations (Third-party services)
- Headless WordPress (Decoupled architecture)
API Endpoints
POST /wp-json/jwt/v1/token– Login and get access tokenPOST /wp-json/jwt/v1/refresh– Refresh access tokenGET /wp-json/jwt/v1/verify– Verify token and get user infoPOST /wp-json/jwt/v1/logout– Logout and revoke refresh token
Security
- Stateless Authentication – JWT tokens contain all necessary information
- HTTPOnly Cookies – Refresh tokens stored securely, inaccessible to JavaScript
- Token Rotation – Refresh tokens automatically rotate on use
- Configurable Expiration – Set custom expiration times
- IP & User Agent Tracking – Additional security metadata
Support
For support and documentation, visit: https://github.com/juanma-wp/jwt-auth-pro-wp-rest-api
Privacy Policy
This plugin stores user session data including IP addresses and user agent strings for security purposes. This data is used solely for authentication and security monitoring.
Screenshots

Admin configuration interface

Security settings panel
Token management dashboard