Limit the number of login attempts possible both through normal login as well as using auth cookies.
By default WordPress allows unlimited login attempts either through the login page or by sending special cookies. This allows passwords (or hashes) to be brute-force cracked with relative ease.
Limit Login Attempts blocks an Internet address from making further attempts after a specified limit on retries is reached, making a brute-force attack difficult or impossible.
Features
- Limit the number of retry attempts when logging in (for each IP). Fully customizable
- Limit the number of attempts to log in using auth cookies in same way
- Informs user about remaining retries or lockout time on login page
- Optional logging, optional email notification
- Handles server behind reverse proxy
- It is possible to whitelist IPs using a filter. But you probably shouldn’t. 🙂
Translations: Bulgarian, Brazilian Portuguese, Catalan, Chinese (Traditional), Czech, Dutch, Finnish, French, German, Hungarian, Norwegian, Persian, Romanian, Russian, Spanish, Swedish, Turkish
Plugin uses standard actions and filters only.
Screenshots
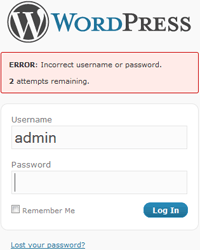
Loginscreen after failed login with retries remaining
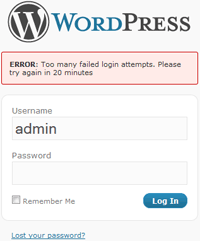
Loginscreen during lockout
Administration interface in WordPress 3.0.4