Mokomaro Login Guard Lite temporarily restricts password logins after five failed attempts from the same connection address within a fixed 15-minute window. Restrictions last 15 minutes. Successful logins clear that connection’s counter.
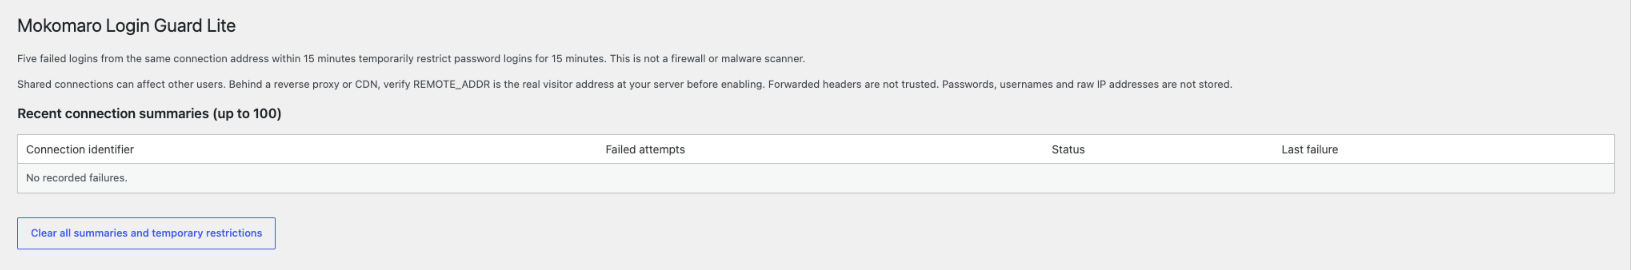
Administrators can review up to 100 recent connection summaries and clear all counters and restrictions under Settings > Mokomaro Login Guard Lite.
All included functionality is free without a trial period. There are no locked premium features, remote license checks, telemetry, external libraries, external update servers or external API requests. This plugin does not include AI analysis, a firewall, malware scanning or file integrity monitoring.
Use only one login limiter at a time. Disable any previous version or other login-limiting plugin before enabling this plugin.
Privacy and data retention
The plugin stores an HMAC-SHA256 connection identifier derived from REMOTE_ADDR and a site secret, failed-attempt counts, window and restriction expiry timestamps, and the most recent failure timestamp in a local database table. This identifier is pseudonymous, not anonymous. Raw IP addresses, usernames, passwords, request bodies and user agents are not stored. Administrators see a shortened identifier. Daily WP-Cron cleanup removes summaries older than seven days when no restriction is active; low-traffic sites may run cleanup later. Uninstall removes this plugin’s table and scheduled task. Deactivation stops the task and retains records.
Important limitations
Verify REMOTE_ADDR identifies the real visitor at the web server before enabling, especially behind a CDN or reverse proxy. Forwarded headers are deliberately ignored. Shared IP addresses can restrict legitimate users. This initial version supports single-site installations only. Password resets remain available; administrators with no active session can wait for the restriction to expire or disable the plugin using their hosting file manager. This is a login limiter, not comprehensive site protection. Application passwords, external SSO and authentication systems bypassing WordPress’s authenticate/wp_login_failed hooks are outside scope. Other authentication plugins may affect behavior; test compatibility first.
Screenshots