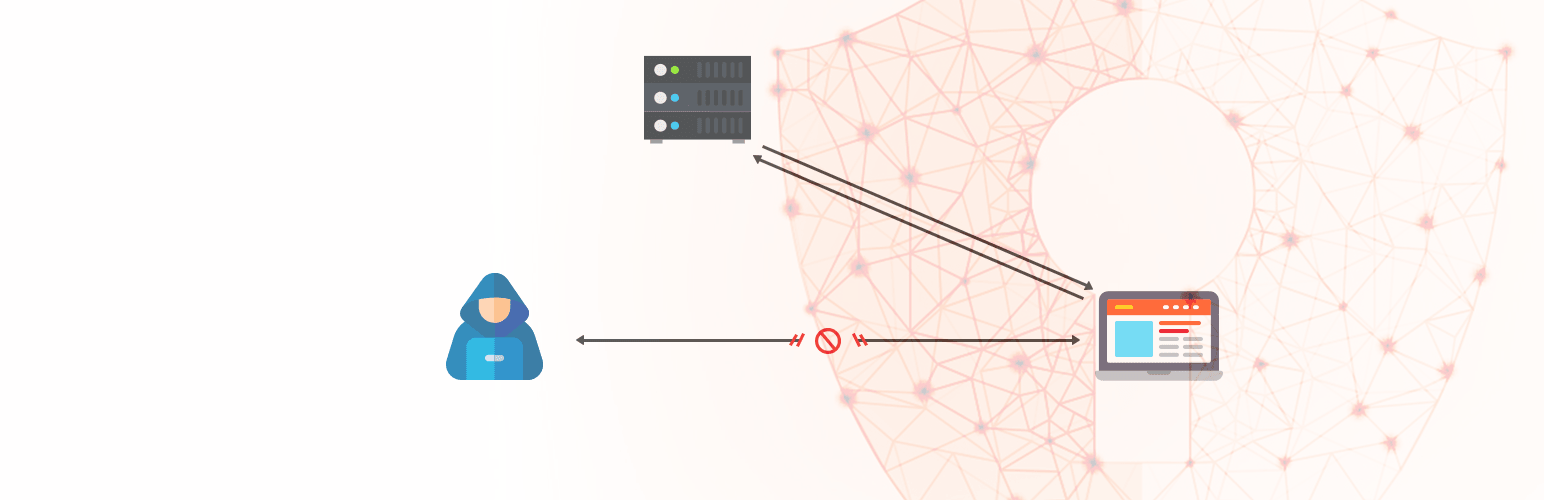
This plugin helps safeguard your website against two common types of Cross-Site Scripting (XSS) vulnerabilities:
- Reflected XSS: This happens when harmful scripts are hidden in a website’s URL. If a user clicks a link with such a script, it can run in their browser, potentially stealing their data or taking control of their system.
- Self-XSS: This occurs when a user’s own input on your website is displayed back to them in an unsafe way, allowing malicious scripts to run in their browser.
This plugin provides several layers of protection:
Blocking: When active, the plugin checks URLs for specific characters. If it finds any of these characters in the URL, it redirects the user to prevent a potential XSS attack. You can customize which characters to block or allow.
- Opening Round Bracket
( - Closing Round Bracket
) - Less than Sign
< - Greater than Sign
> - Opening Square Bracket
[ - Closing Square Bracket
] - Opening Curly Bracket
{ - Pipe or Vertical Bar
| - Closing Curly Bracket
}
Encoding: For an extra layer of security, the plugin encodes certain characters found in URL parameters. This stops harmful code from running, even if it’s present in the URL. You can also choose to exclude specific parameters from being encoded.
- Exclamation Mark
! - Double Quotation
" - Single Quotation
' - Opening Round Bracket
( - Closing Round Bracket
) - Asterisk Sign
* - Less than Sign
< - Greater than Sign
> - Grave Accent “`
- Cap Sign
^ - Opening Square Bracket
[ - Closing Square Bracket
] - Opening Curly Bracket
{ - Pipe or Vertical Bar
| - Closing Curly Bracket
}
Escaping HTML in $_GET: This plugin automatically makes HTML characters safe within the $_GET variable. This is vital if your website pulls data from URLs and displays it as part of your web page. It helps prevent malicious scripts from being injected through user-provided input.
Important Notes:
- After activating the plugin, thoroughly test your website forms, especially if you use WooCommerce. Make sure the plugin doesn’t interfere with your shopping cart and checkout processes.
- We welcome bug reports for this plugin on GitHub: https://github.com/samiahmedsiddiqui/prevent-xss-vulnerability/issues. Please remember that GitHub is for bug reports only, not general support.
By using this plugin and following these recommendations, you can significantly improve your website’s defense against XSS attacks.
Screenshots
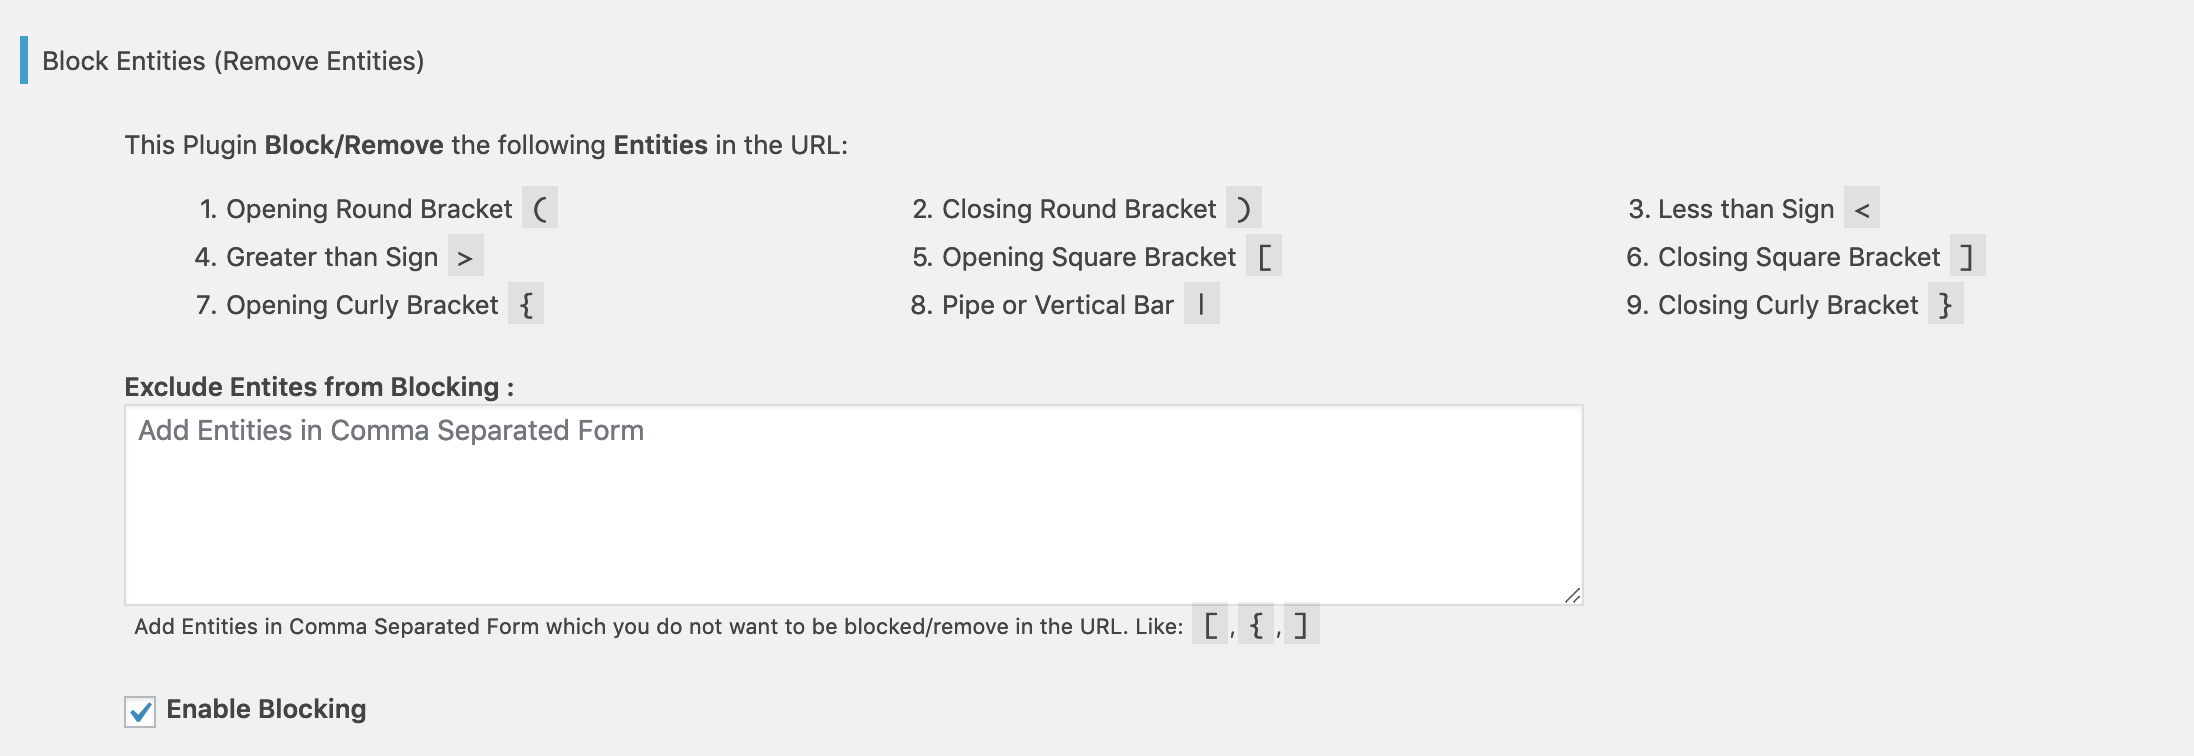
It removes the parameters from the URL which are used in XSS Attack and redirects the user (Recommended).
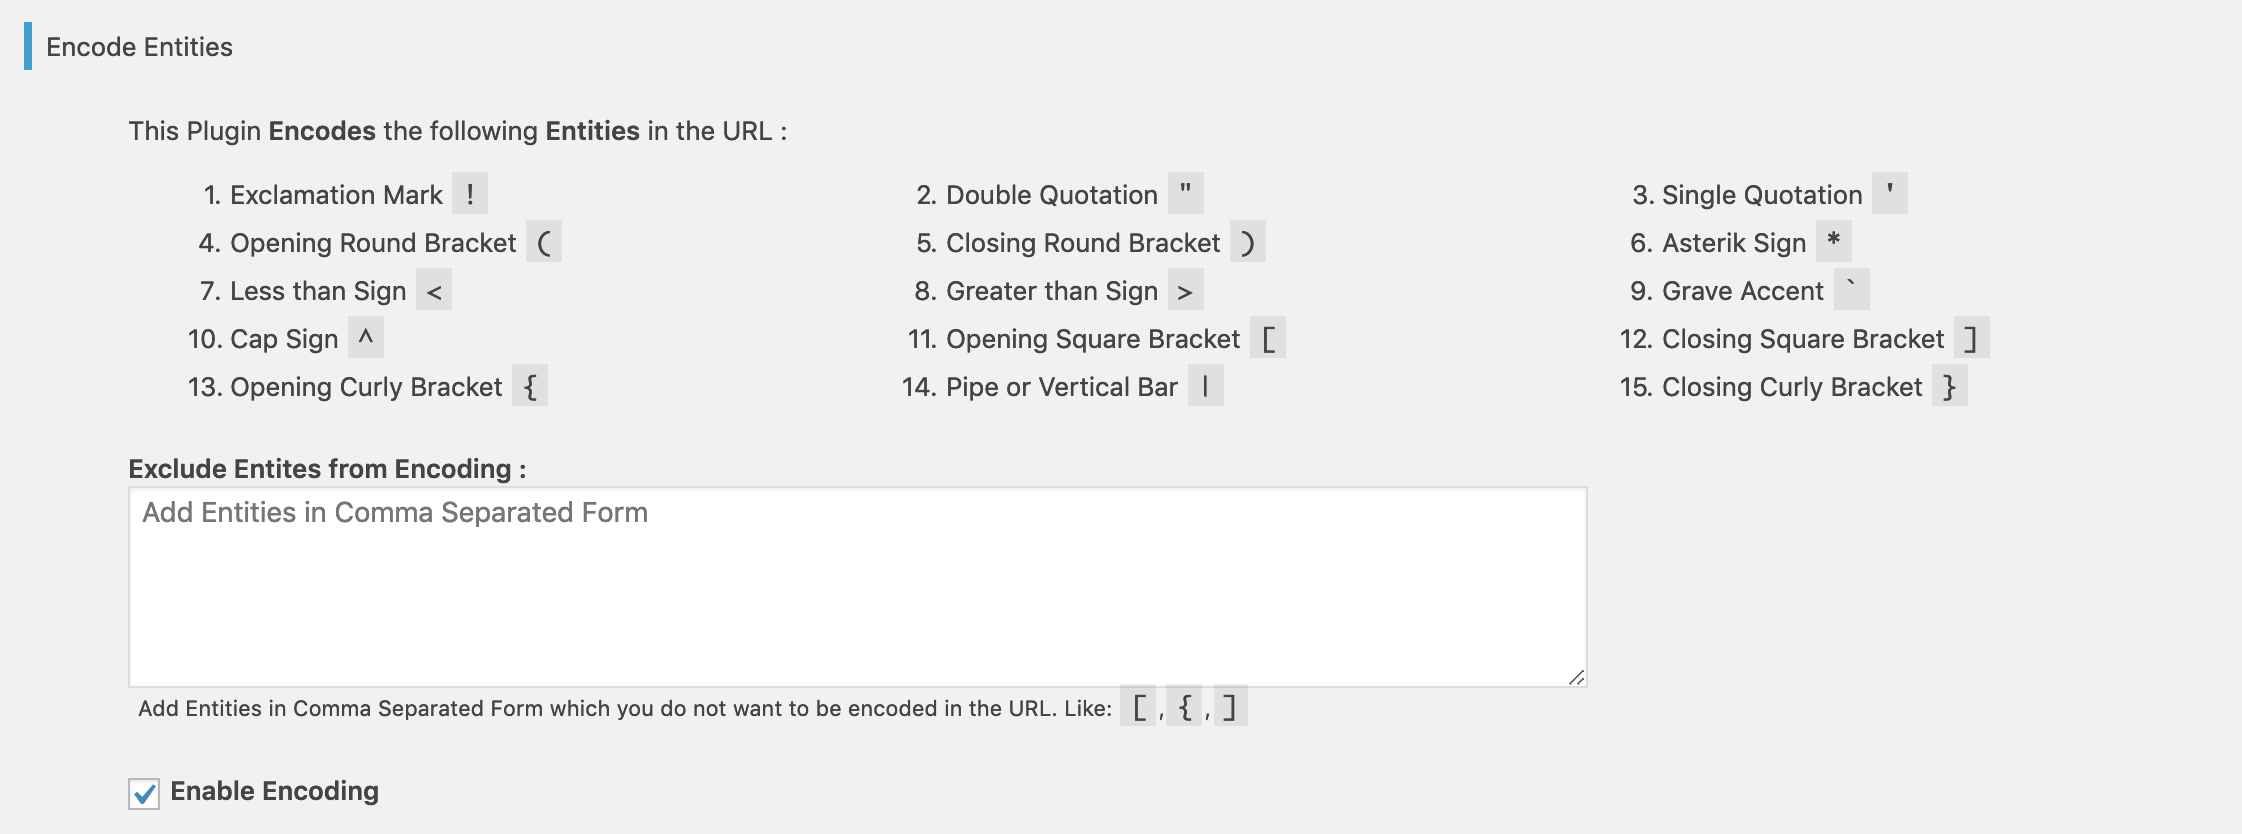
It encodes the parameters from the URL which are used in XSS Attack.
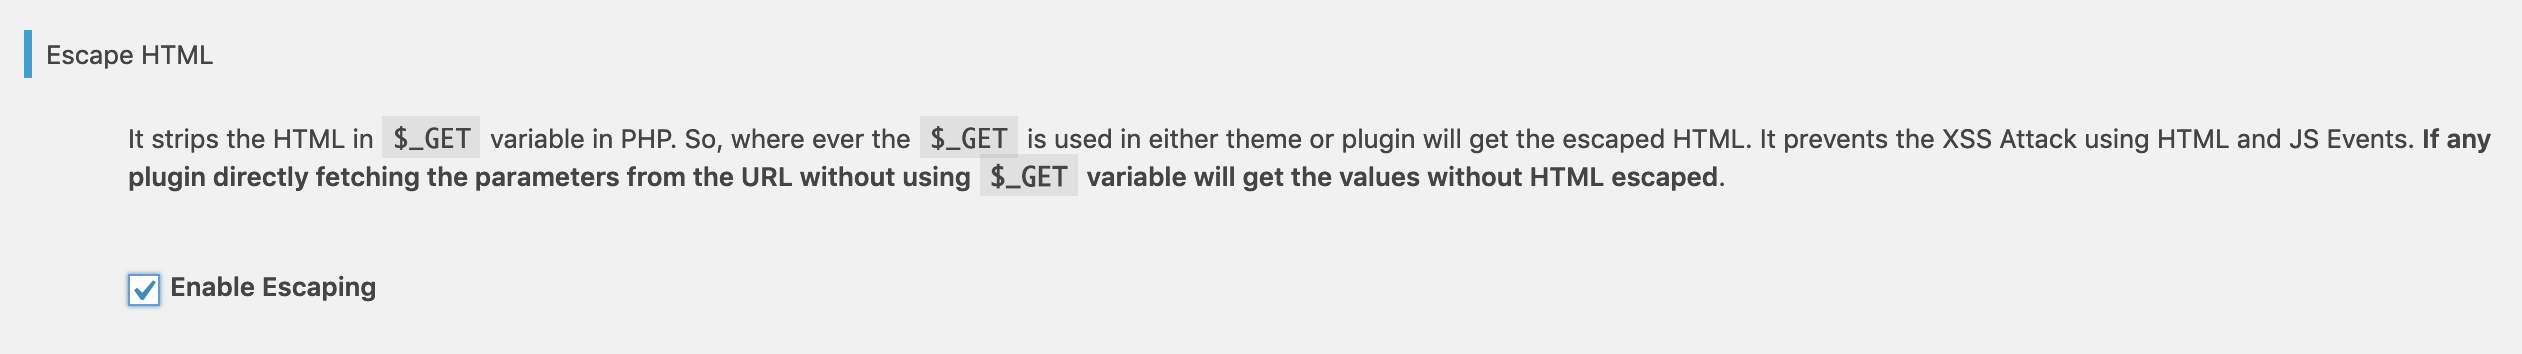
It escapes the HTML from the $_GET PHP variable which is mostly used to read the data from the URL (Recommended).
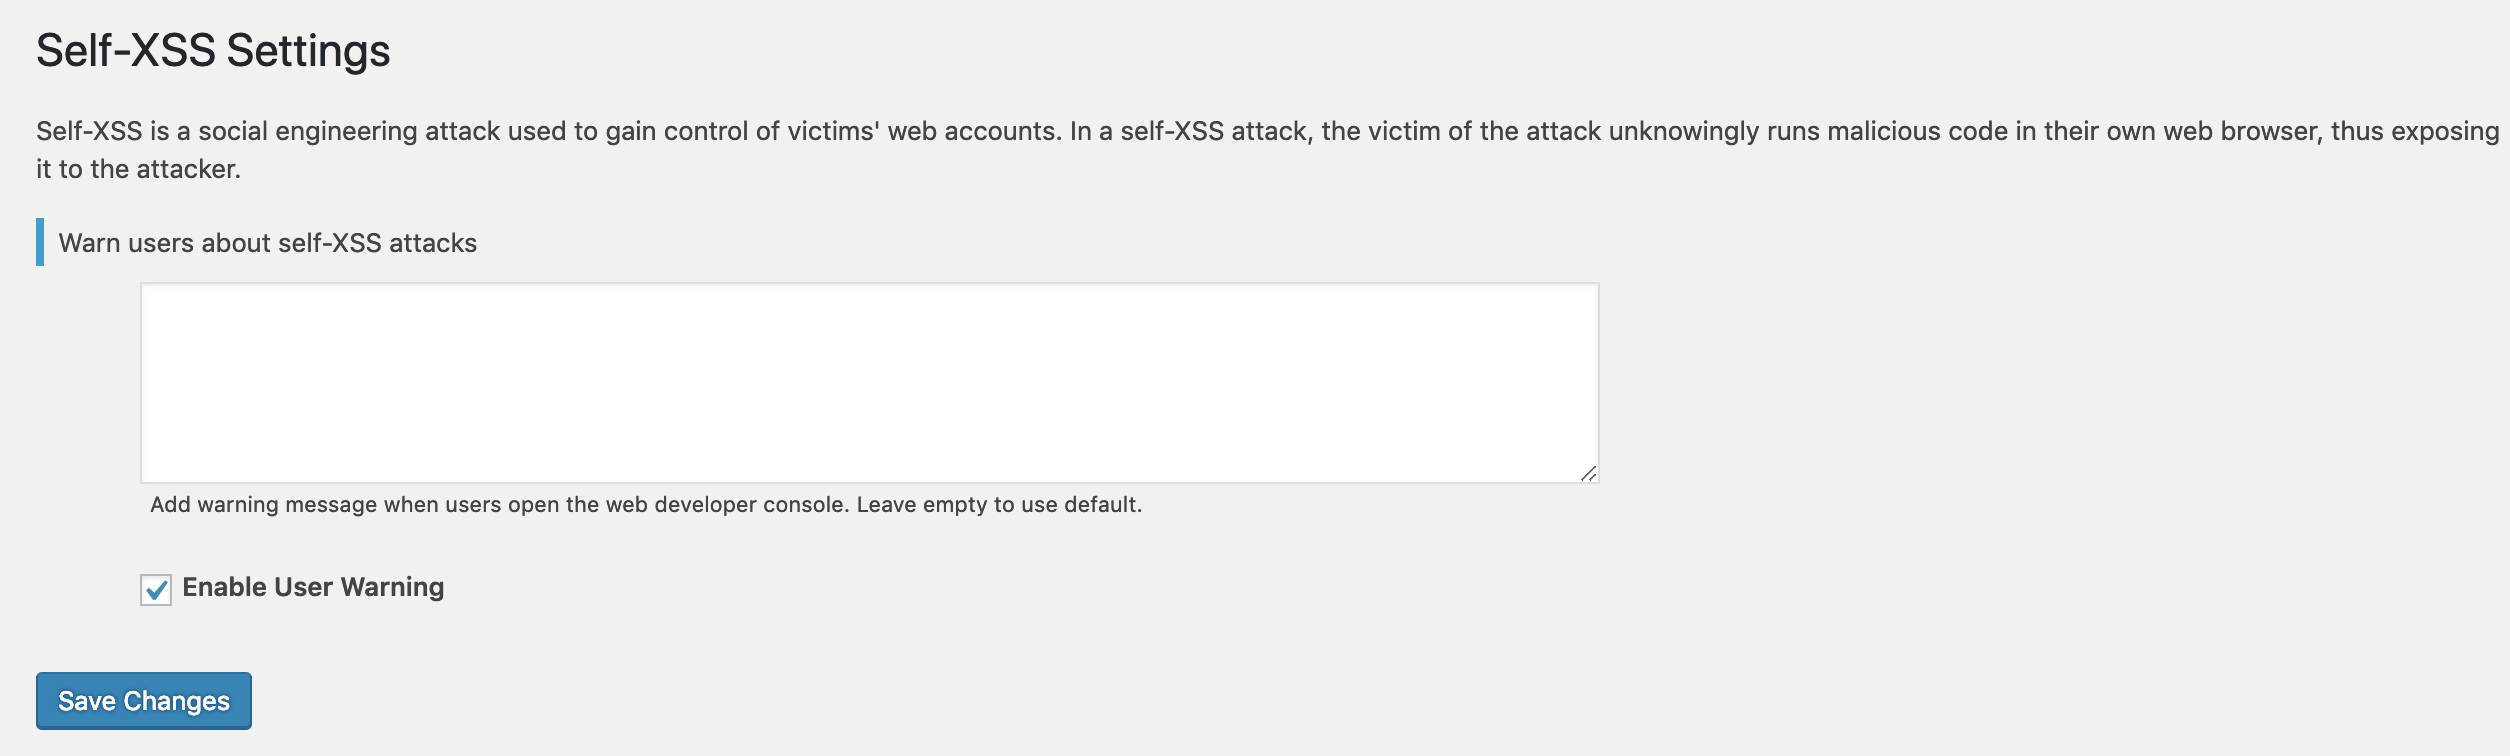
Add the message in developer console for the user to alert about the XSS attack.

Show message in developer console to alert user about the Self-XSS attack. This message can be customized from the settings page.