SiteAssure monitors WordPress functions that support enquiries and sales. Local checks work without an account; optional cloud monitoring adds independent checks, uptime, centralized alerts and reporting.
Free local monitoring
- Daily and on-demand assurance scans, a dashboard, diagnostics and Site Health checks.
- Protected plugins and business functionality, including payment, mail, booking, membership and page-builder dependencies.
- Critical-page publication, availability, content baselines and supported builder-markup checks.
- Form inventory, configuration, frontend presence and real submission outcomes, without retaining submitted field values.
- Contact Form 7, WPForms, Gravity Forms, Formidable Forms, Elementor Pro Forms and Divi Contact Forms integrations. Local validation and mail-handoff coverage vary by provider.
- WooCommerce gateway registration, availability and expected-gateway monitoring.
- Plugin, theme, core, selected settings and user-access change history, with incident timelines and recoveries.
- Post-update checks and confirmation of update-associated fatal errors or unexpected plugin inactivity.
- WordPress mail success/failure counters, optional handoff tests and an automatic cloud-backed email delivery check when recent form testing has not already verified delivery.
- Optional email alerts, recovery messages, weekly summaries, configurable history retention and a local report export.
Selected forms remain monitored when a page placement disappears or the form is unpublished or deleted. These changes are reported separately from email-configuration warnings so the administrator can review them or explicitly stop monitoring.
Checks do not guarantee availability, delivery or payment processing. A local mail handoff does not prove receipt.
Optional SiteAssure Cloud
Free, Pro and Agency cloud plans have different monitoring, schedule, history and transaction allowances. Paid features perform work in the external service; the local plugin does not expire.
Browser visibility checks do not submit forms. Eligible controlled form transactions require an administrator to start a test or enable its schedule. They submit generated test values through the supported provider, reroute test notifications to a unique SiteAssure receiving address, and suppress supported CRM, opt-in, webhook, registration and other downstream actions for that signed request. Temporary provider entries are removed where controlled storage is supported. Results identify actions that were suppressed rather than tested. Unsupported actions can make a form ineligible. Production CAPTCHA challenges are not solved as a human.
Formidable user-registration tests suppress registration and its dependent notifications and instead send a separate WordPress mail-transport probe. Elementor Atomic Forms require a supported version and Email action. Divi Email Opt-in/Signup modules are excluded. Pure opt-in forms without an independently verifiable email action remain visibility-only. Custom integrations can behave differently; complete a successful manual test before scheduling recurring tests.
The cloud WooCommerce journey checks products, cart, checkout and gateway controls without placing orders or attempting payments. Gateways that show payment controls only after Place Order cannot be fully verified. Up to three checkout profiles can cover different products, locations, currencies or gateway combinations. An optional least-privilege Assurance Test User requires administrator approval. HTTP Basic Authentication credentials can be supplied for protected staging sites.
External services and connection consent
The optional SiteAssure service is operated by WPAssist. Installing or activating the plugin does not contact it. An administrator must choose to connect; clicking the email-verification control sends the pairing request, and ongoing reporting starts after verification.
- Website: https://www.wpsiteassure.com/
- API: https://api.wpsiteassure.com/v1
- App: https://app.wpsiteassure.com/
- Terms: https://www.wpsiteassure.com/terms/
- Privacy: https://www.wpsiteassure.com/privacy/
Connection sends the website URL, supplied verification email and software/version information. Once connected, signed HTTPS requests send heartbeats (normally every ten minutes), scan results, minimized diagnostic messages and evidence, capabilities, selected monitor definitions, notification preferences, reporting periods and aggregate weekly counters. Heartbeats also include the server hostname and server address so the service can coordinate browser security-challenge recovery for sites in the same account on the same host. The service immediately converts these inputs to a keyed fingerprint and does not retain either source value. The plugin polls for authorized commands and retries temporarily failed reports.
When no controlled form email has reached SiteAssure within seven days, the authenticated heartbeat may provide a one-use receiving address and opaque reference for an automatic email delivery backup check. WordPress sends a privacy-safe test message to that address and reports whether its mail API accepted the handoff. The cloud records whether the message arrived, allows time for delayed hosting mail, and can alert or recover the resulting delivery incident. The message contains no visitor, customer or form-submission data, and its body is not retained by the monitoring database. A recent verified controlled form email suppresses this backup message.
Form definitions contain provider IDs, names, public placement and last-known URLs, lifecycle and transaction-eligibility status, selectors, inactivity settings and successful real-submission timestamps. Critical-page definitions contain configured URLs, content word-count baselines and intentional-edit revision tokens, not page text. WooCommerce monitoring additionally sends eligible product/variation IDs, public URLs, variation attributes, cart/checkout URLs and expected gateway IDs and labels.
Authorized form tests exchange generated values, bounded provider/action identifiers, suppression and cleanup outcomes, and test email with the service. If expressly approved, staging access or generated test-user credentials are sent over HTTPS and stored encrypted locally and by the service. Real customer credentials are not collected. Pausing stops normal reporting; disconnecting removes local pairing credentials. Local monitoring continues.
Privacy and local data
Local settings, scan results, activity and incident history stay in the WordPress database. Local activity can identify the administrator responsible for a change. Cloud scan evidence omits actor attribution and structured sensitive fields; recognizable email addresses, credentials, bearer tokens and query credentials are redacted. Custom diagnostic text may still describe site configuration and is covered by the service privacy policy.
Cloud monitoring does not collect visitor-submitted field values, real customer credentials, configured WordPress mail recipients, message bodies, CAPTCHA keys, mail credentials or visitor IP addresses as monitoring fields. The connected heartbeat’s server address and hostname are used transiently to create a keyed hosting fingerprint and are not stored. Test notifications use generated data. Only bounded action IDs, provider labels, categories and suppression outcomes are reported for downstream integrations; subscriber data, custom action titles, list IDs and provider credentials are excluded.
Connected websites synchronize notification preferences, their revision, weekly-summary timestamps and aggregate counters. Authorized account managers can manage alert, recovery and weekly-summary preferences. The adaptive email delivery backup is automatic while cloud reporting is active. WordPress notification recipients remain local; cloud notifications use account recipients. Local alerts use WordPress mail. The cloud sends connected weekly summaries, with a local fallback if reporting is unavailable.
History retention is configurable. Uninstalling preserves local data unless Delete data on uninstall is enabled. Disconnect the cloud website before removing the plugin if you also want independent cloud monitoring to stop; deleting local data does not delete the service account or its history.
Screenshots

Modern assurance dashboard with score and issue summary.
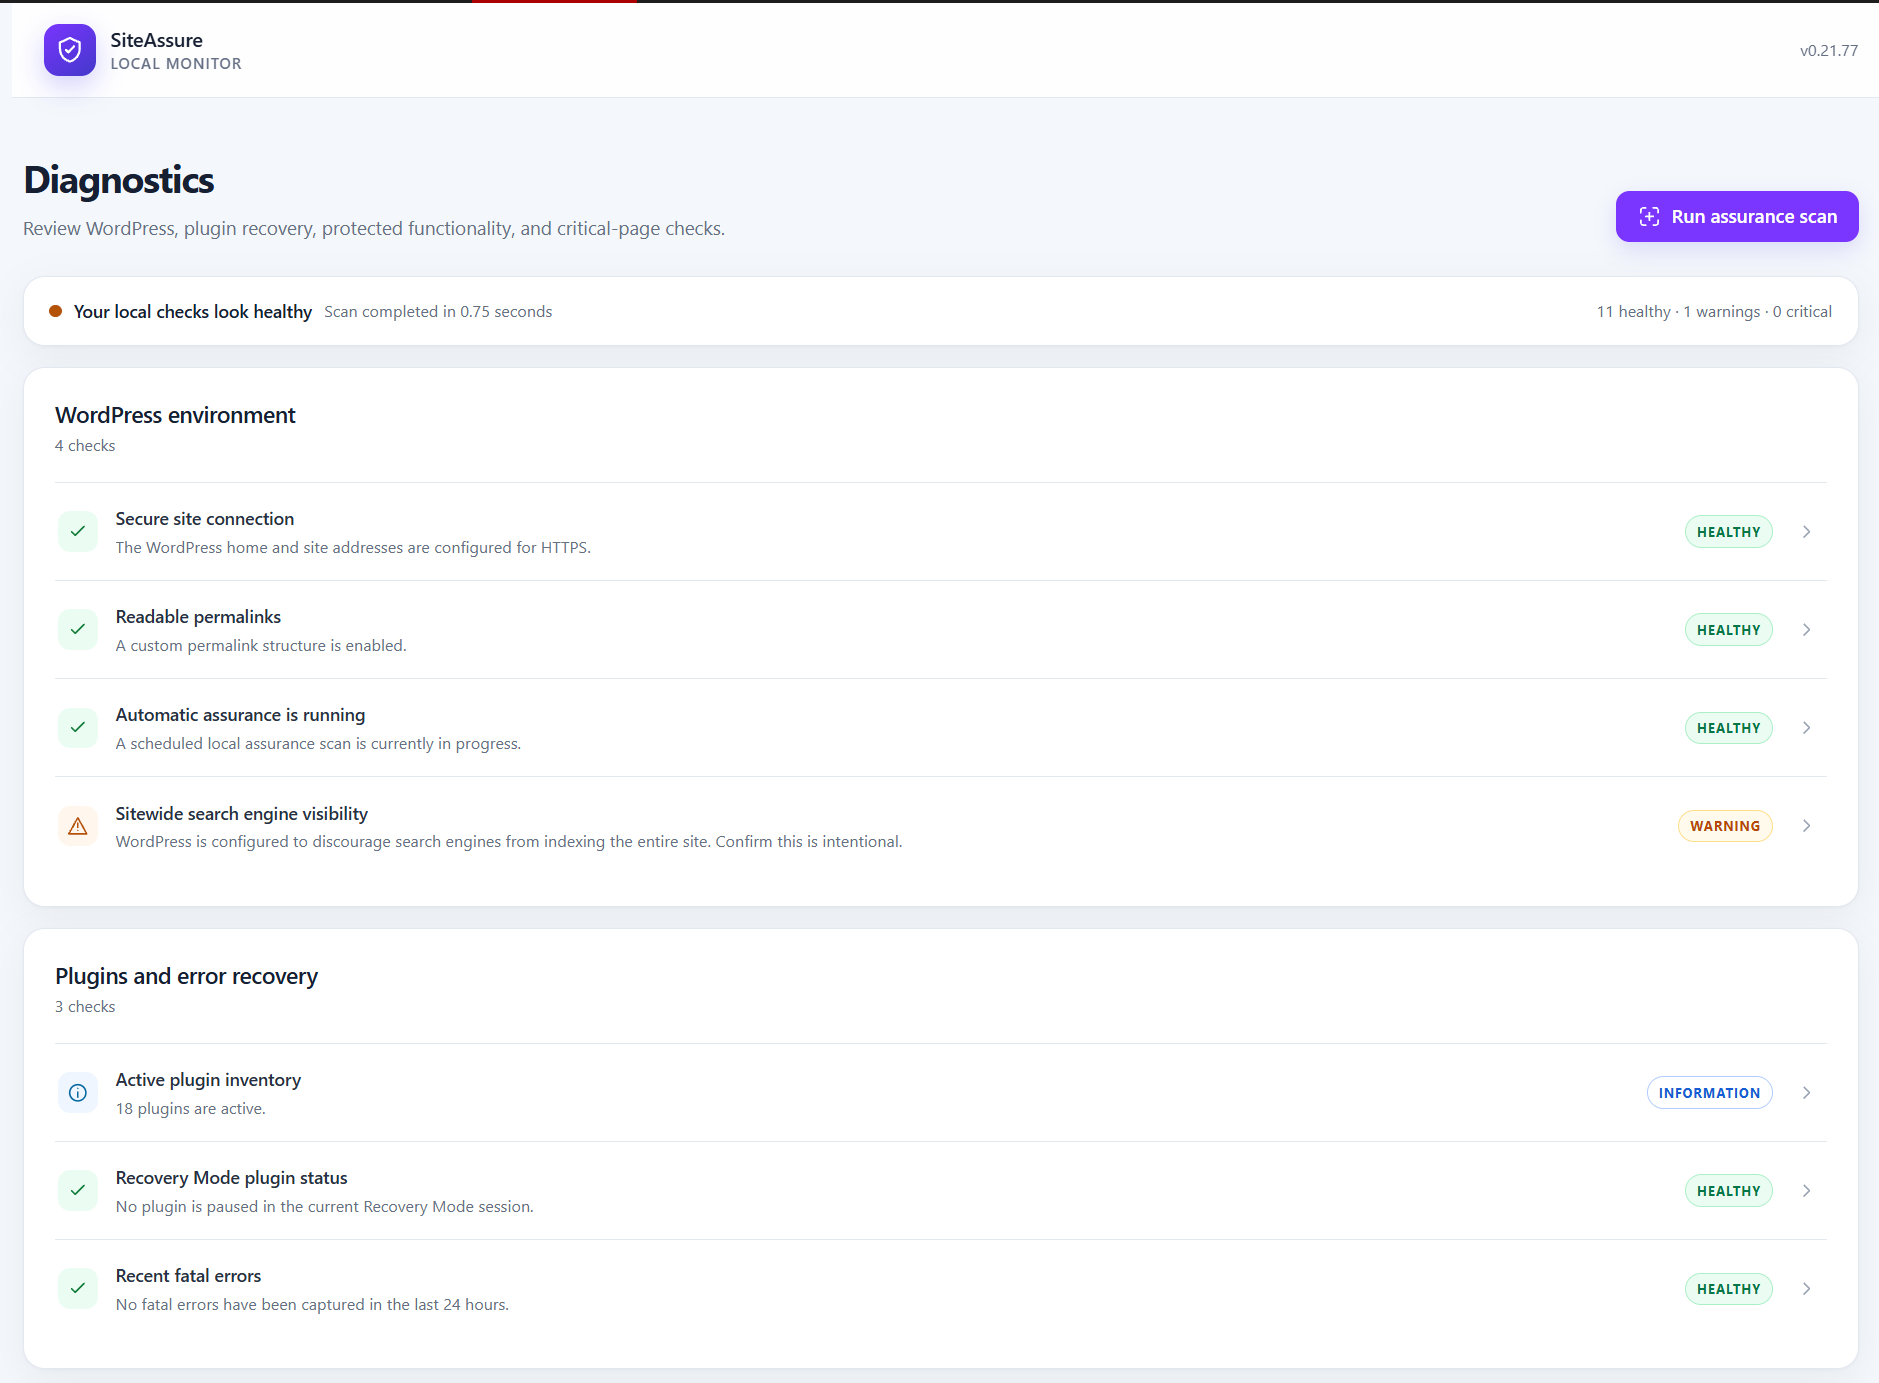
Core diagnostic results with supporting evidence.
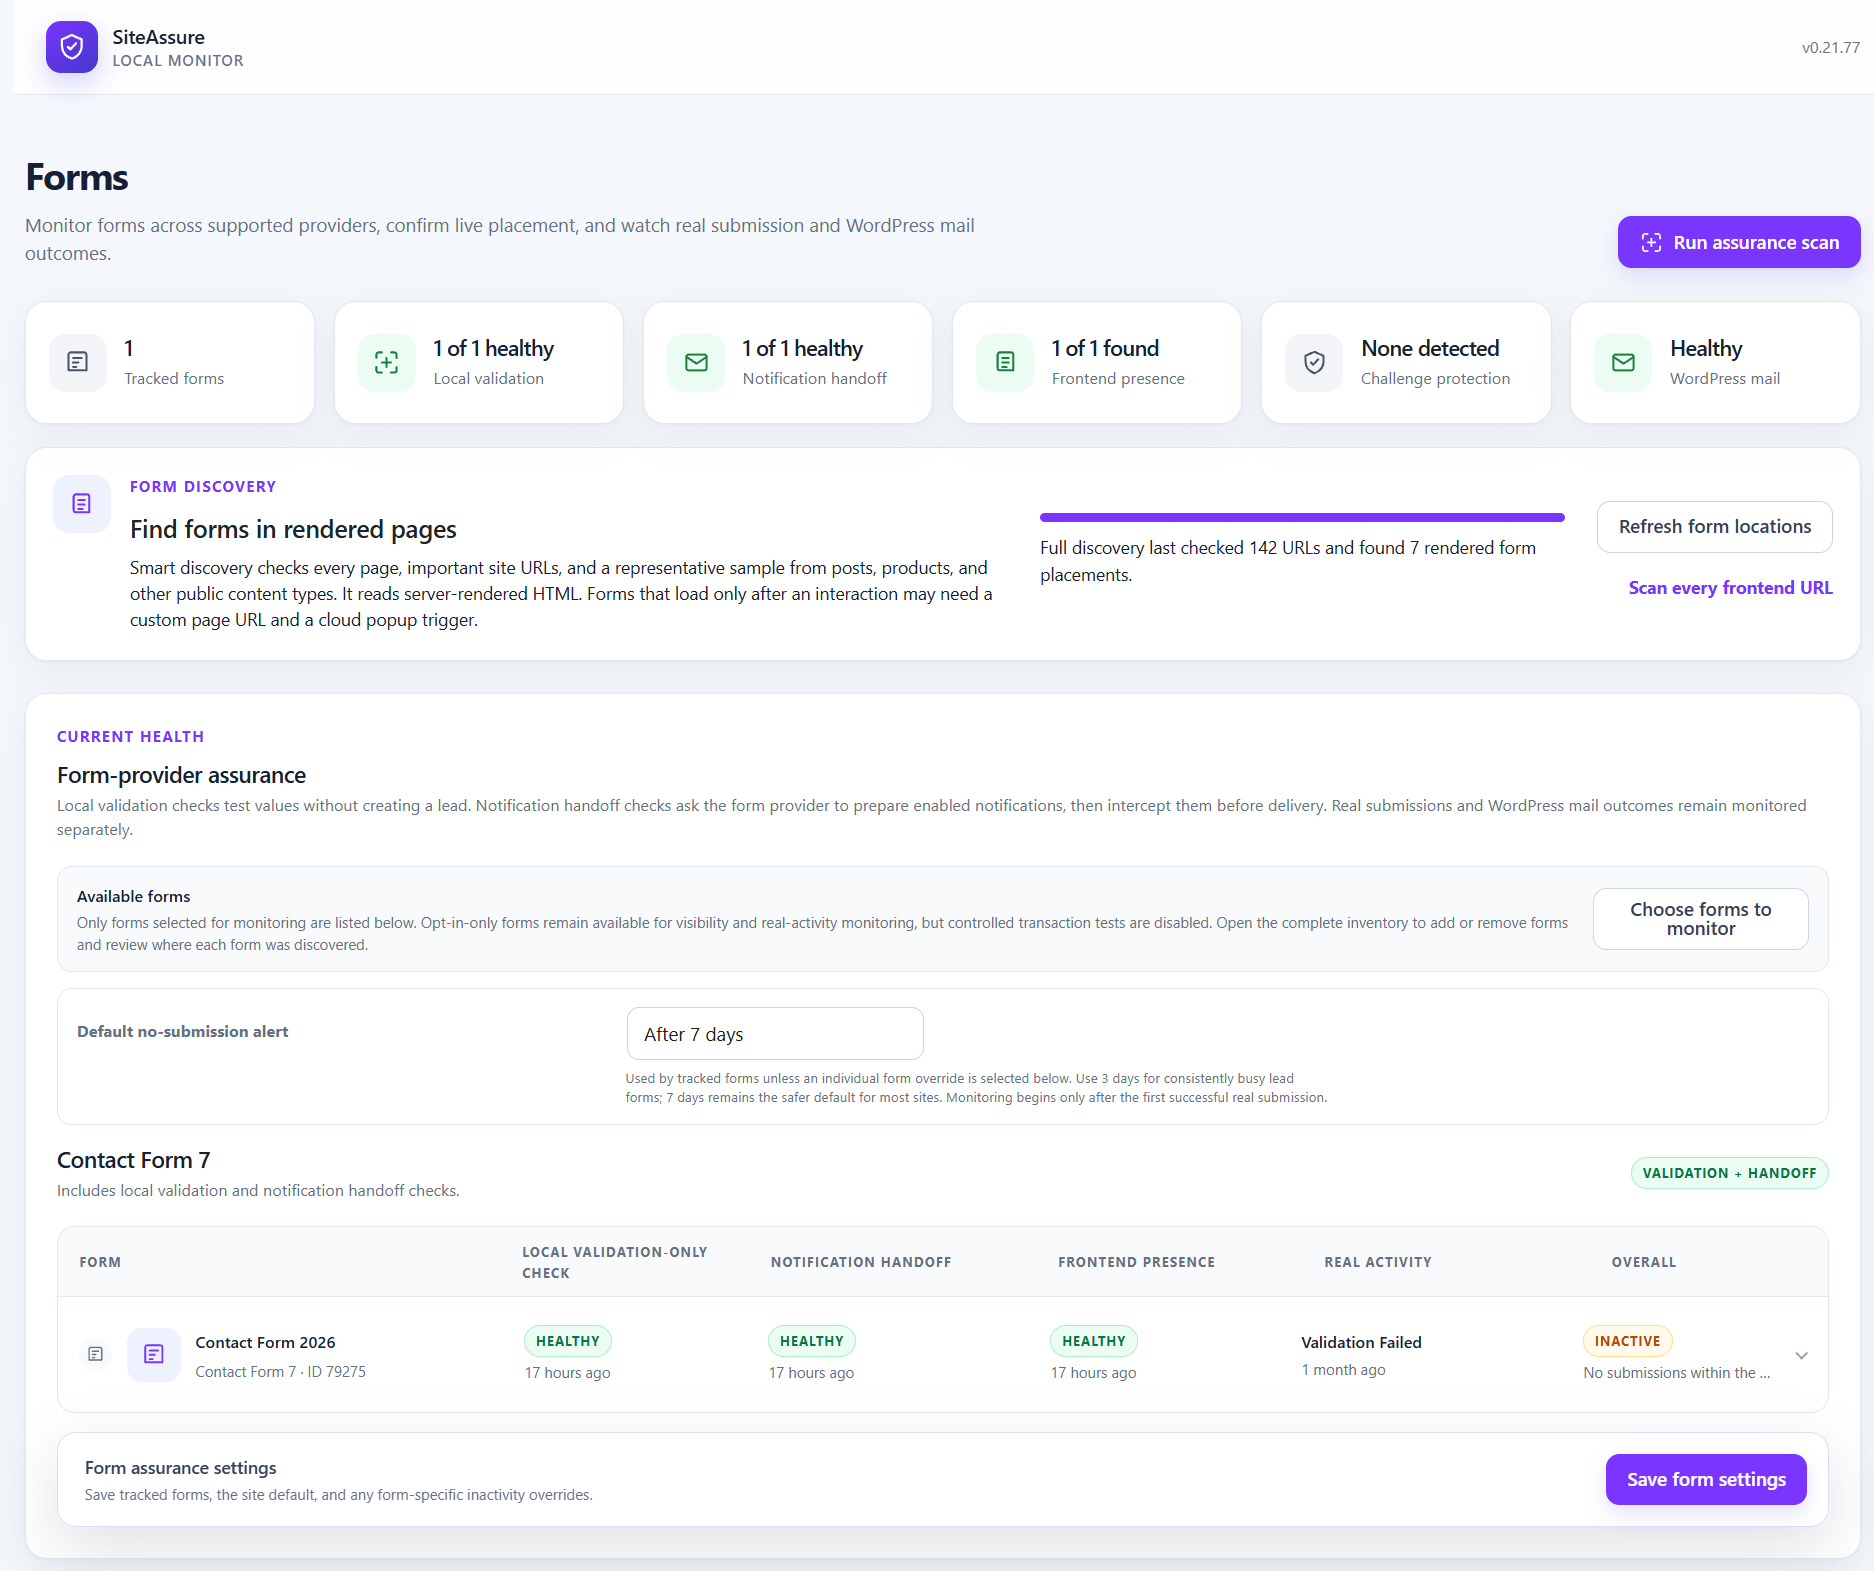
Tracked form assurance, real outcome monitoring, and WordPress mail health.
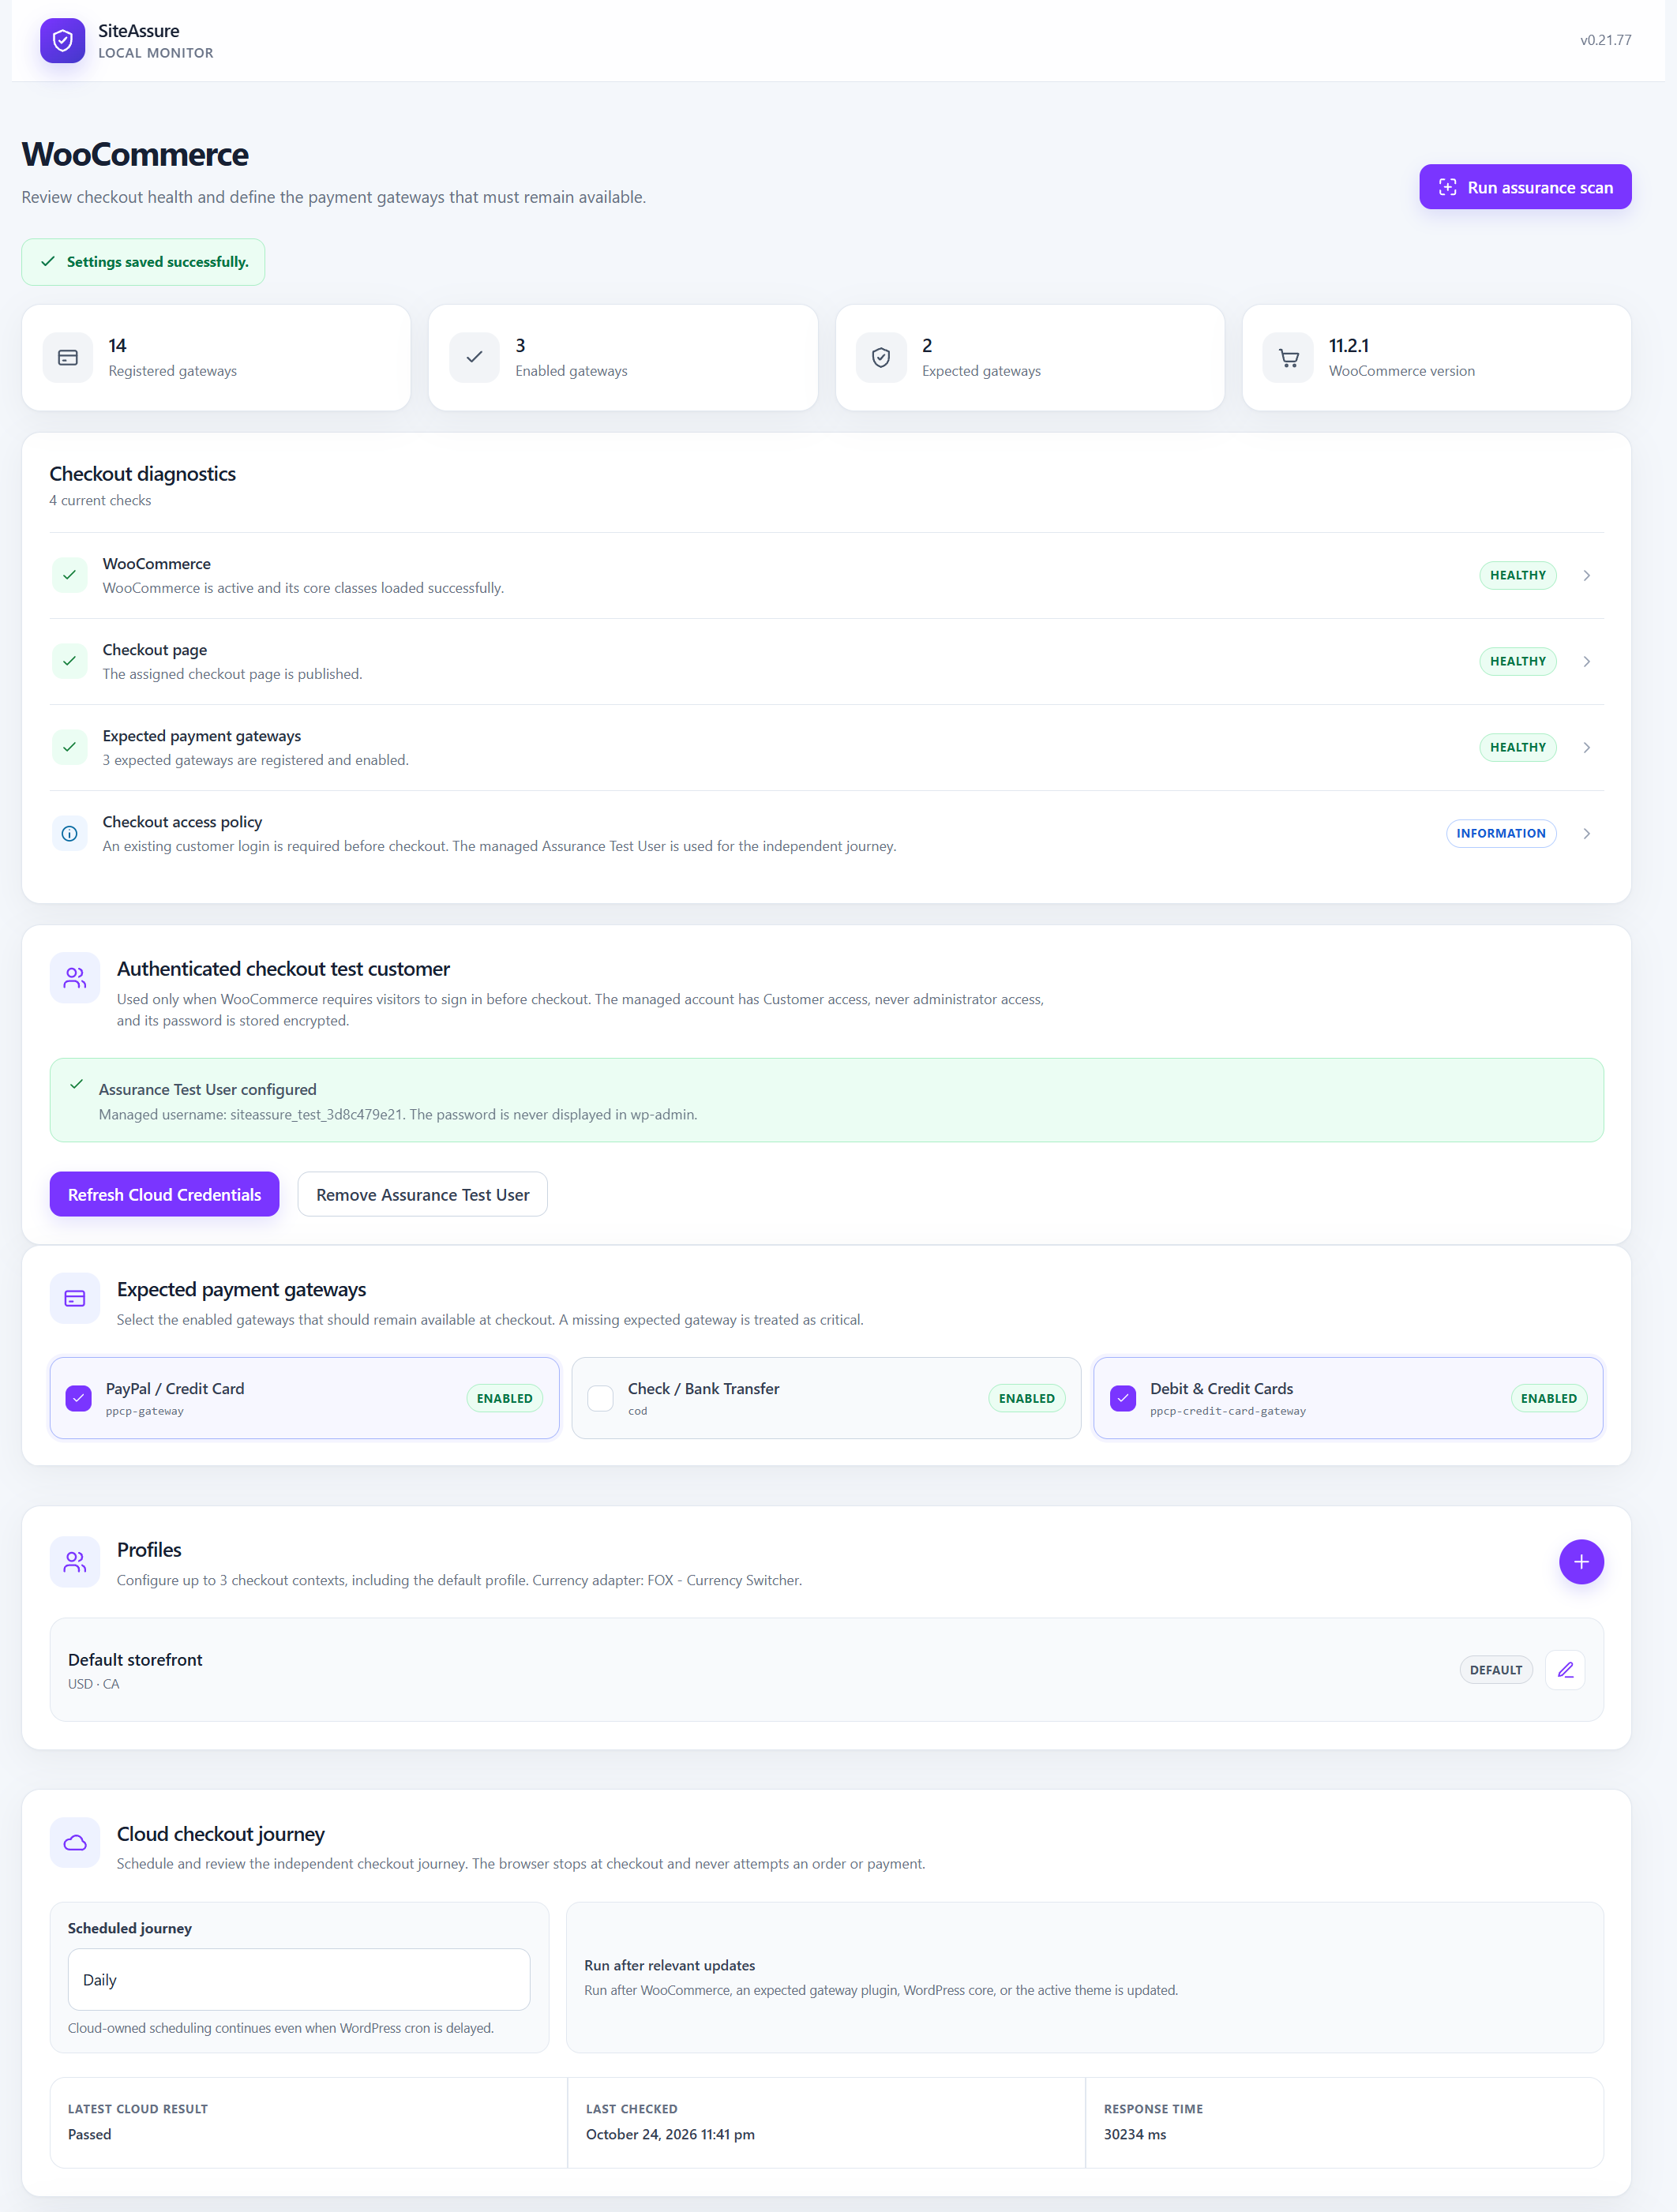
Conditional WooCommerce checkout and gateway screen.
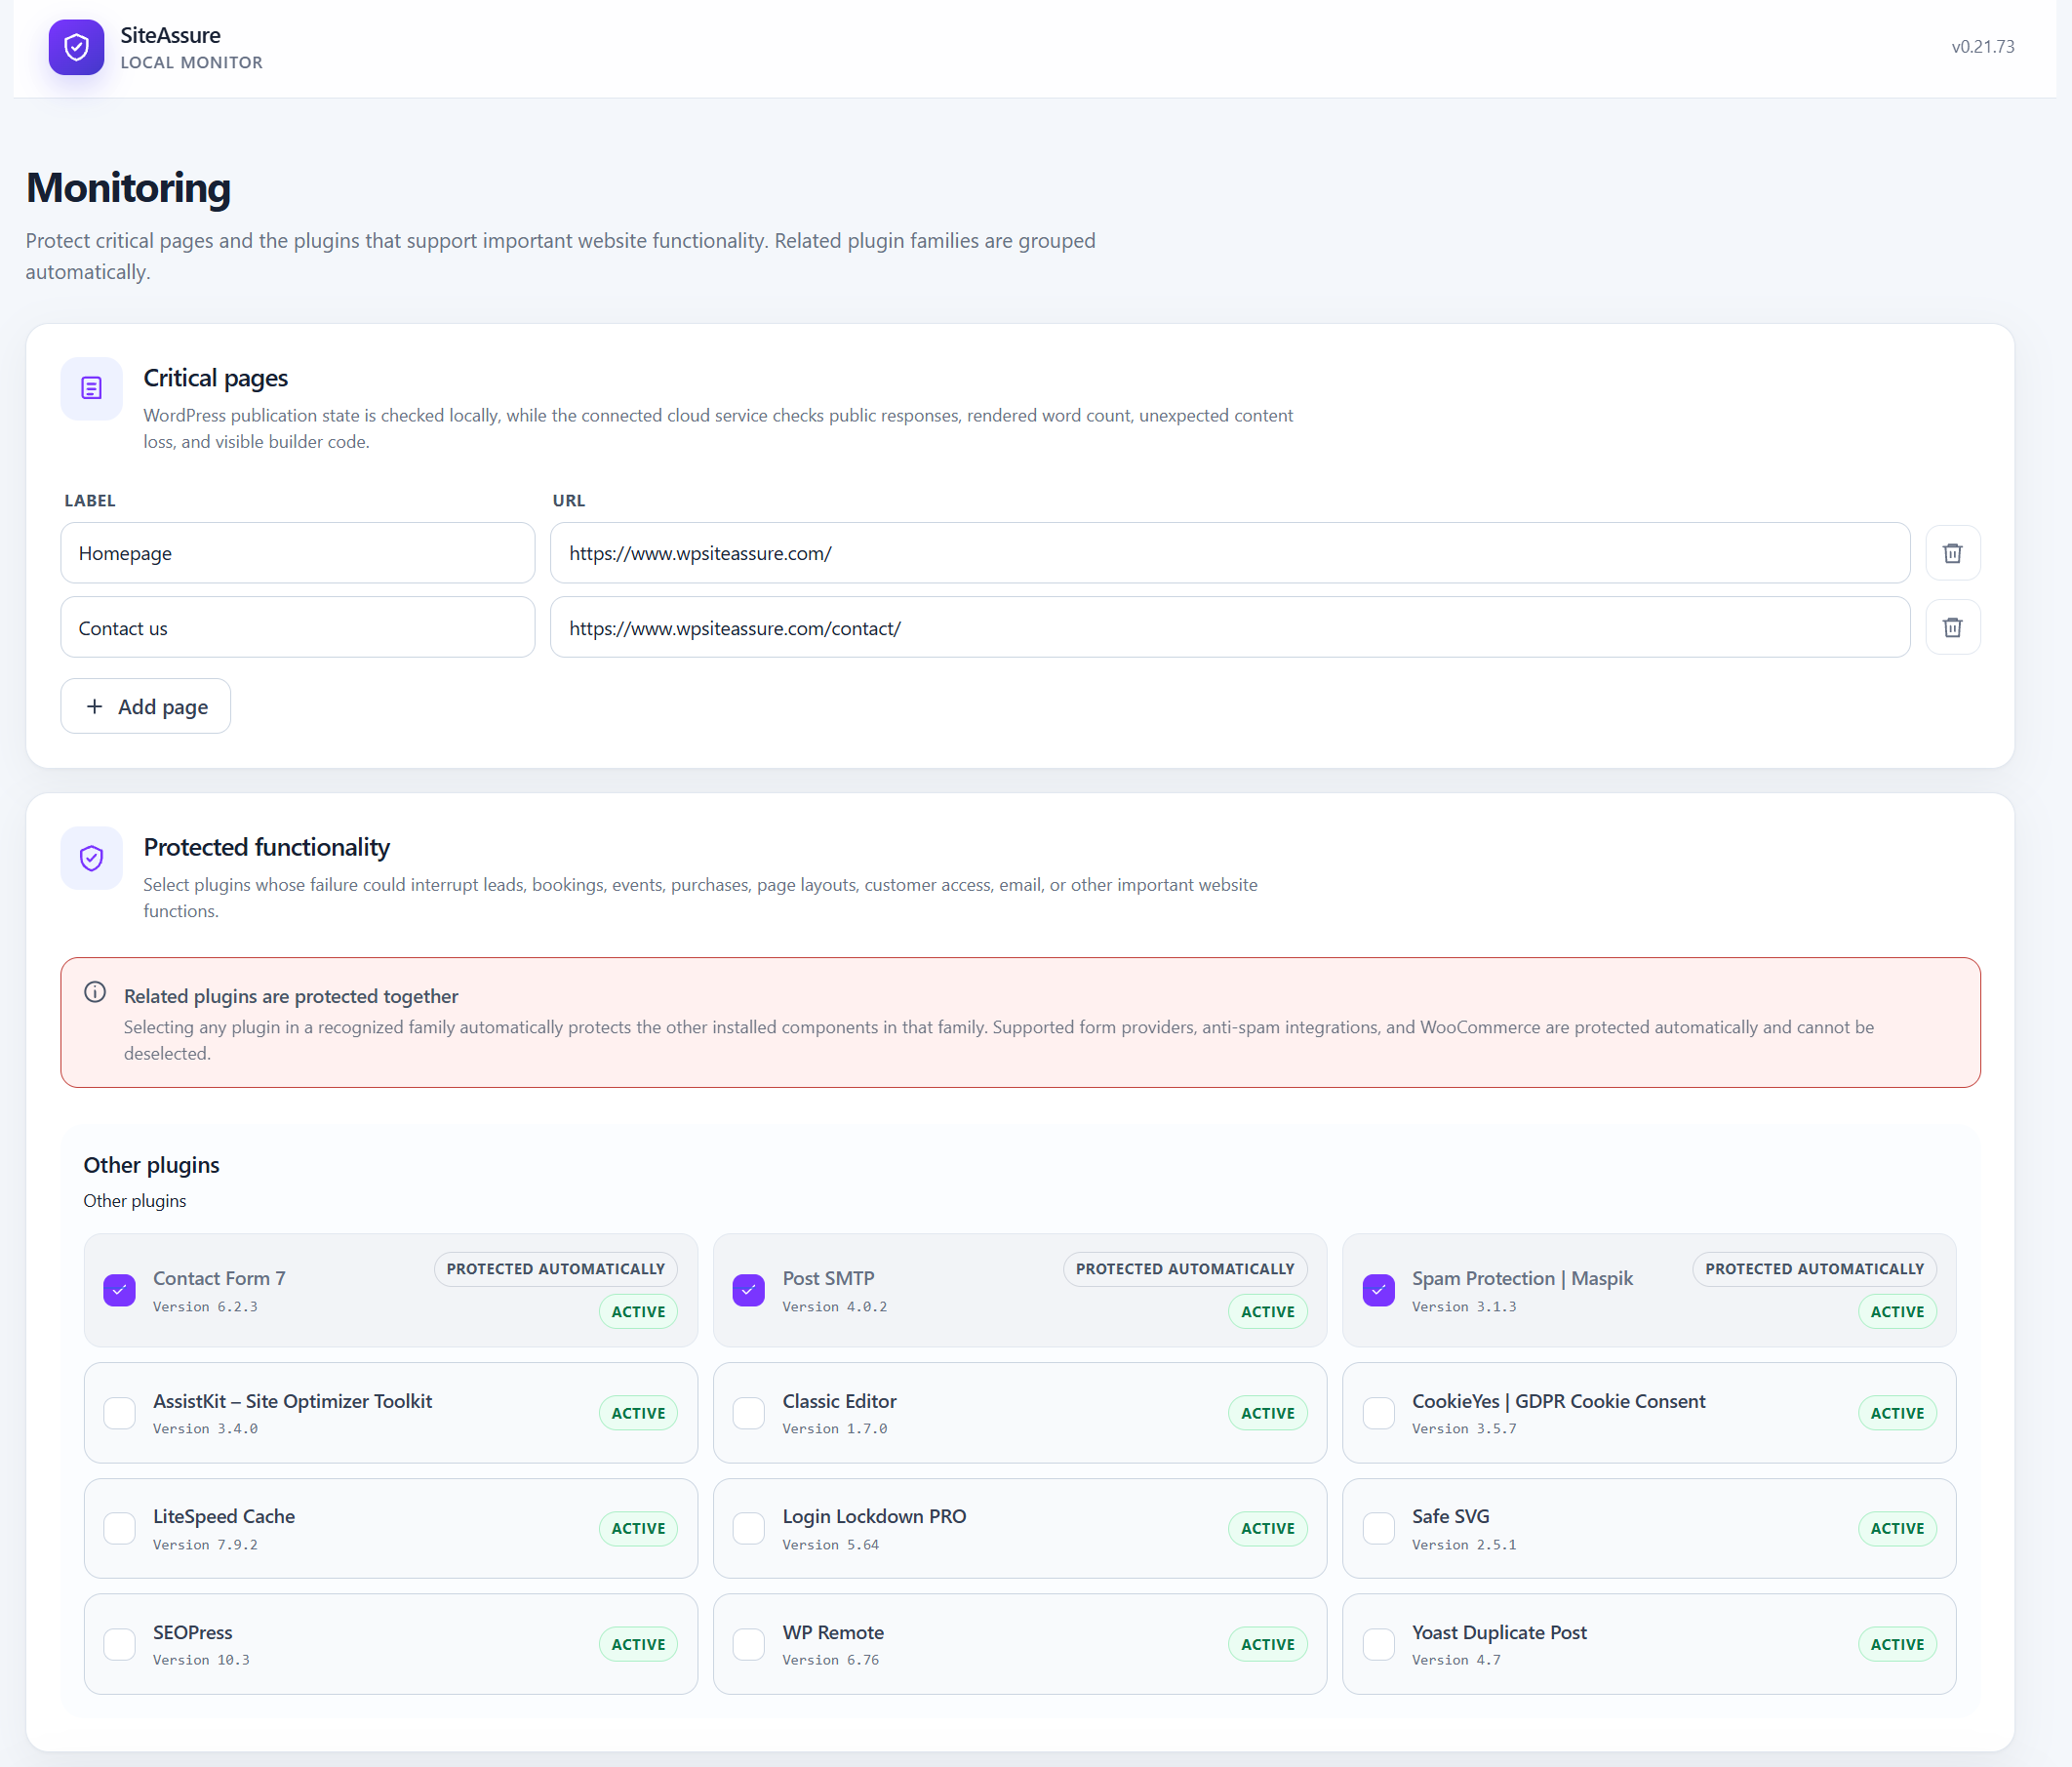
Critical page monitoring configuration.

Curated activity history with area and actor attribution.
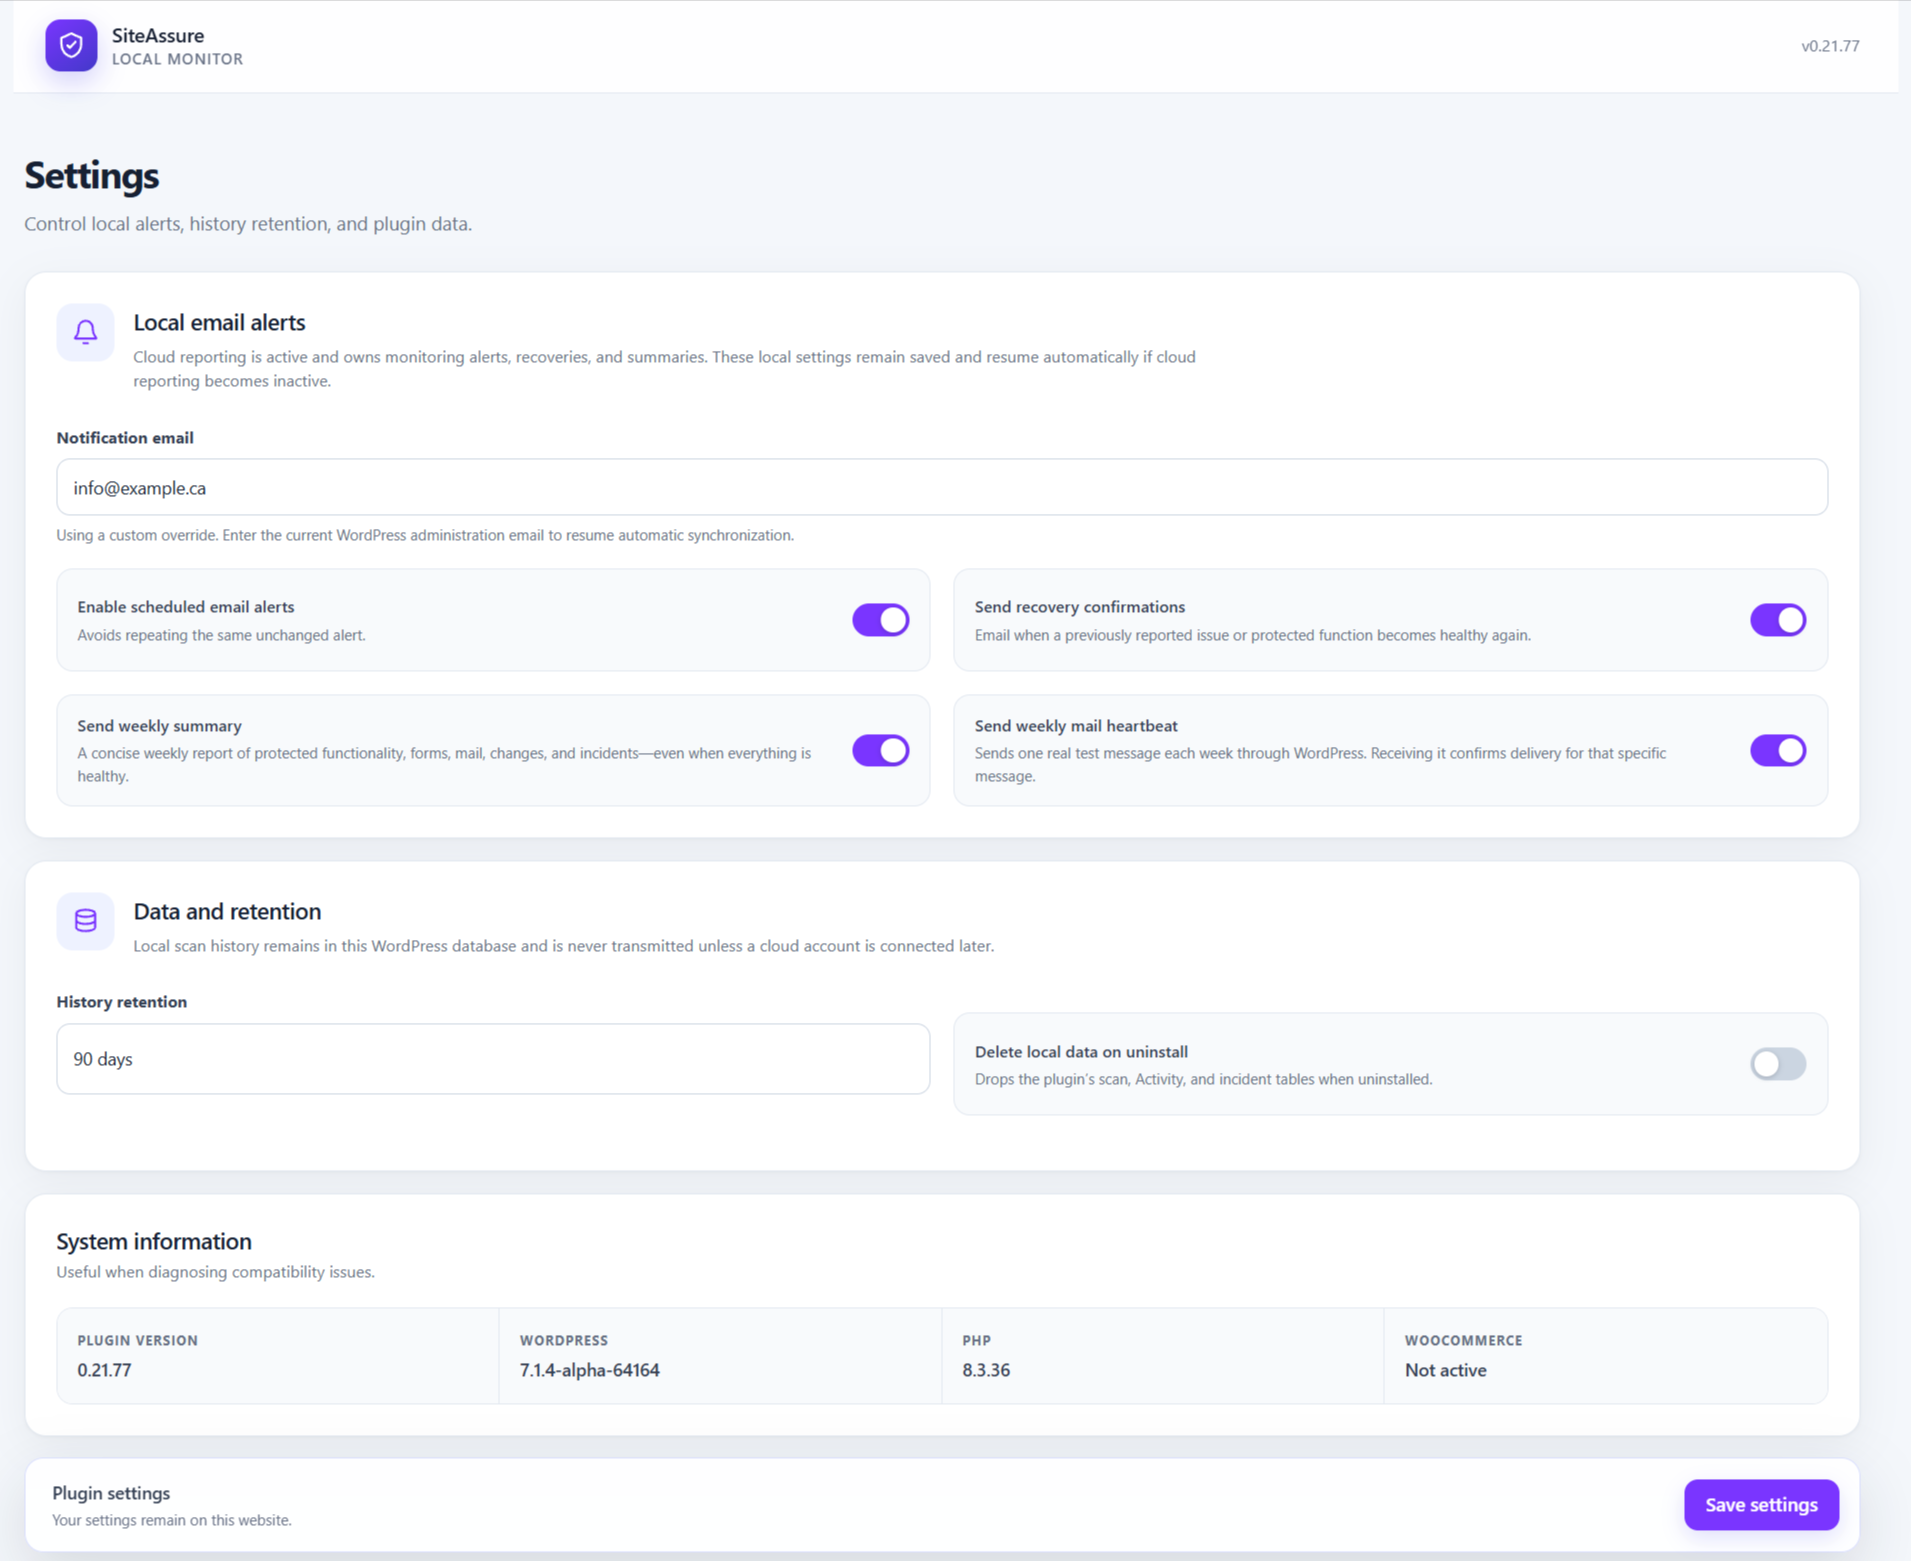
Settings for local email alerts, notification preferences, and data retention.
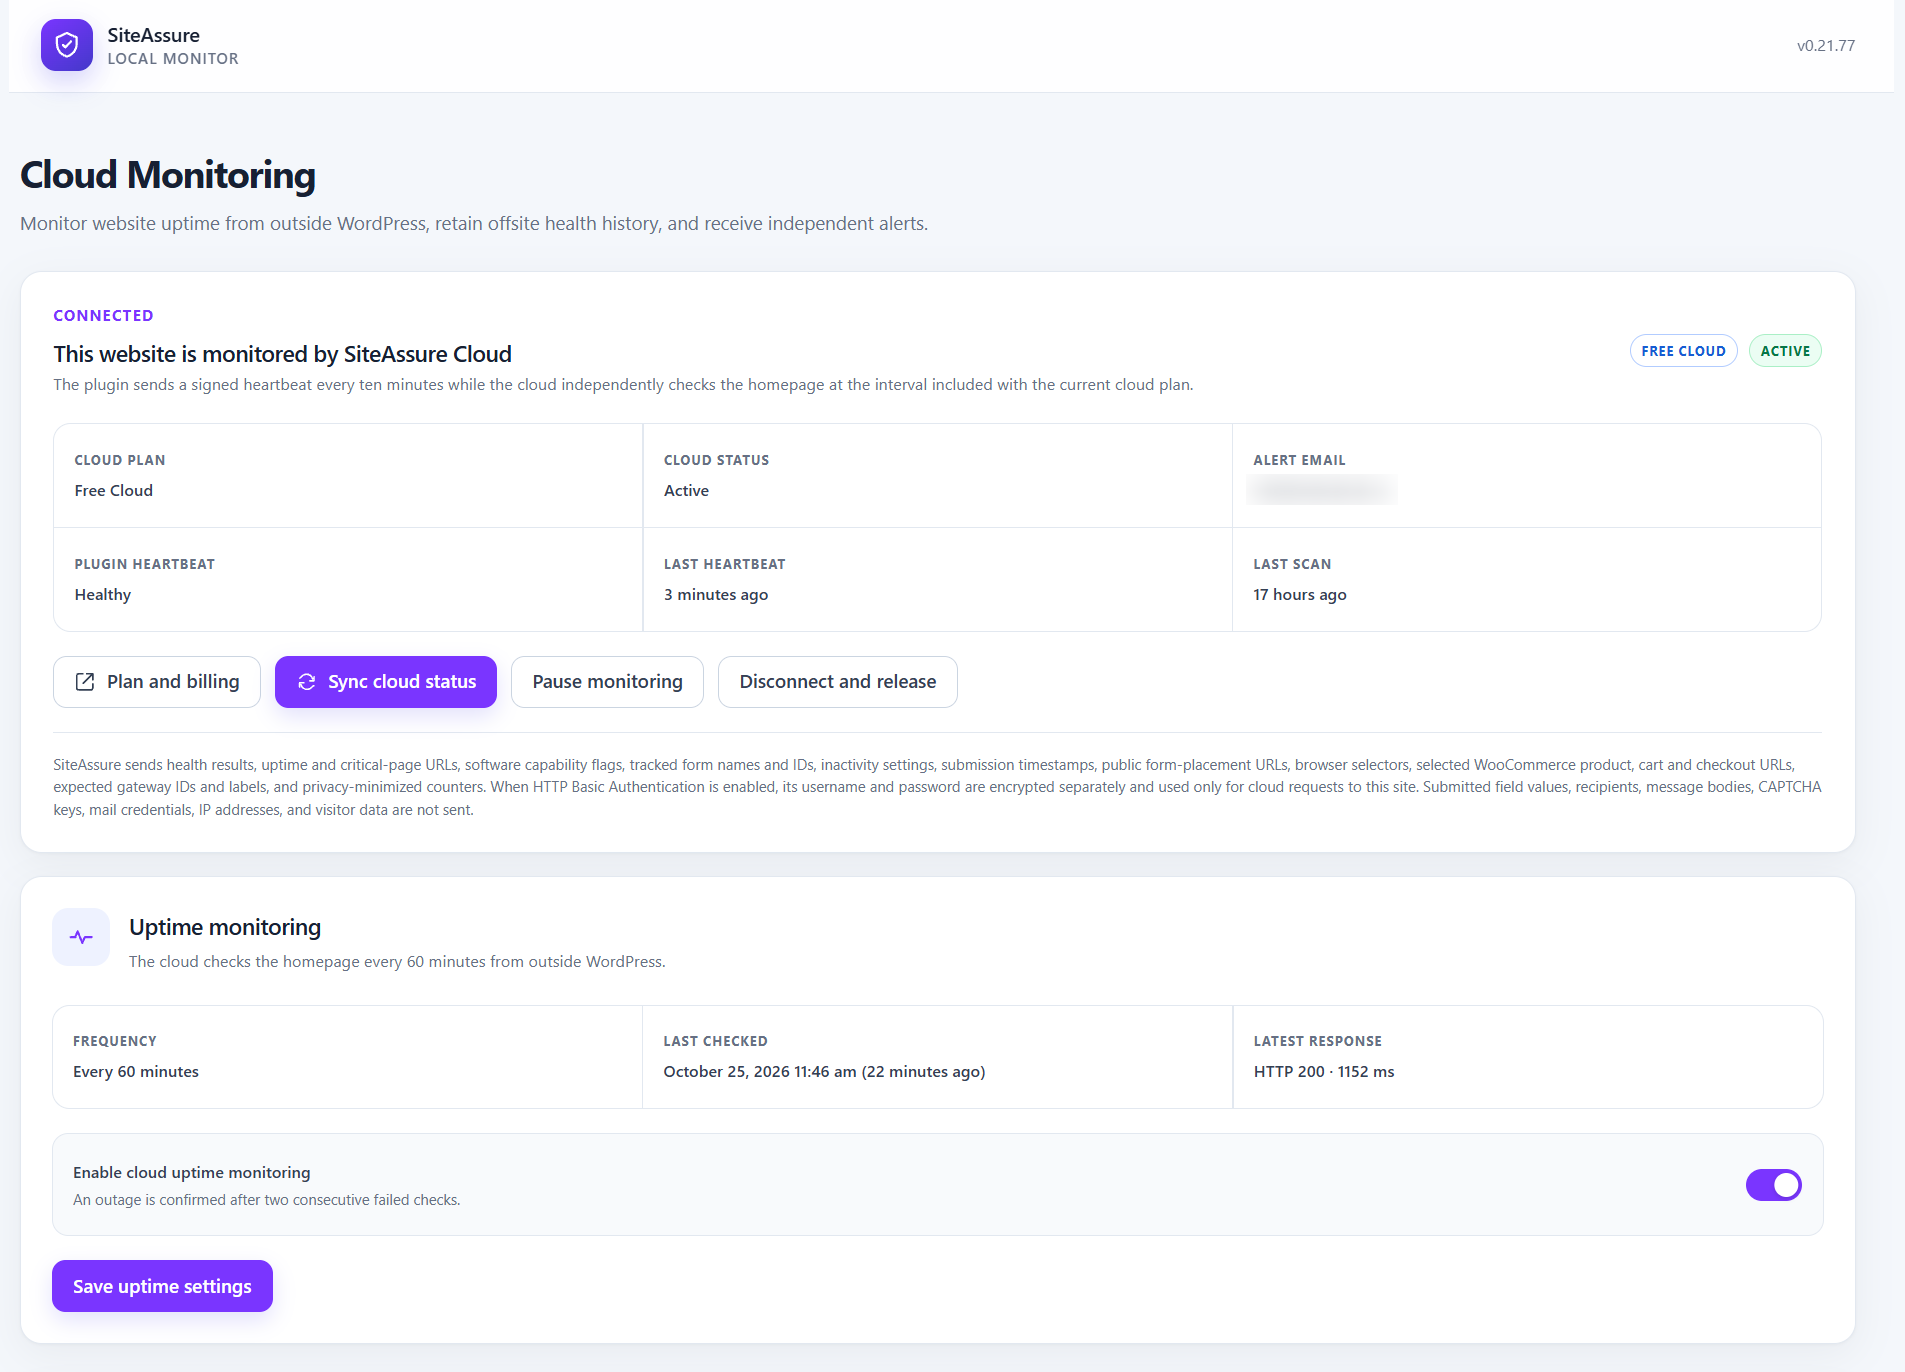
Cloud monitoring connection, lifecycle, and reliability controls.