Ultimate Security – AI Security, 2FA, Login Protection & Vulnerability Scanner
by WP Ultimate Security
Stop hackers and bots from getting into your WordPress site. Ultimate Security adds two-factor login, blocks password-guessing attacks, stops spam bots and warns you about plugins with known security holes. A setup wizard picks the right settings for your kind of site, so you don’t have to understand every option. And because a security plugin should never break your site, every change can be previewed, tried in Test Mode and undone.
It is also built for the age of AI. Check your site for hidden prompt injection aimed at AI agents. See which AI crawlers and AI bots, like GPTBot and ClaudeBot, read your pages, and block AI scrapers with ready-made Cloudflare rules. Connect ChatGPT, Claude or Cursor with read-only access, through a sign-in you approve or the official WordPress MCP Adapter.
Why site owners choose it
- Free, with no account needed. Install it and it works. No sign-up and no usage tracking.
- Set up in about 3 minutes. The wizard asks what kind of site you run, checks it, and shows every change before applying it. You can undo it all later.
- Try before you enforce. Test Mode shows what would have been blocked, without blocking anyone.
- Undo any change. Recent changes lists your last ten saves; undo one in a click. Turn on “Protect my changes” and a sensitive change that breaks your login page or site is undone for you.
- You can’t lock yourself out for good. The wizard gives you an emergency link that switches the plugin off from any browser, and one click adds your own address to the “always allow” lists.
- Act fast after a break-in. Emergency Lockdown stops every plugin, theme and WordPress change for a set time while you clean up, and you get an email when any account is given administrator powers.
- Ready for AI. Find text written to trick AI agents (prompt injection), see which AI bots crawl your site, and let AI apps read your security status without letting them change anything.
Protect your login
Two-factor login. After the password, users confirm with a code sent by email or shown in an authenticator app (Google Authenticator, Authy, Microsoft Authenticator and similar). Choose which user roles need it. Works on the WordPress, WooCommerce and Ultimate Member login forms. See at a glance on the Users screen who has two-factor on. Changing two-factor settings asks for a code first, and you are warned by email if someone keeps failing your two-factor check, because that means they know your password.
Stop password-guessing bots.
- Lock out anyone who gets the password wrong too many times. Repeat offenders wait longer each time.
- Permanently block addresses you never want to see again.
- An administrator can send a locked-out user a 15-minute recovery link, or let users ask for an unlock link by email.
- Works behind Cloudflare automatically. Site Health tells you if your host’s setup needs one extra step.
Hide your login page. Move wp-login.php to a private address so bots can’t find it.
Stronger passwords.
- Set rules for length, letters, numbers and symbols, or pick a ready-made preset.
- Stop people reusing old passwords, and ask for a new one on first login or after a set time.
- Reject passwords that have appeared in known data leaks. The check never sends the password itself anywhere.
- Works with password managers: they are told your rules, so the passwords they create are accepted, and the “Generate password” button follows your rules too.
Control who stays signed in.
- Limit how many devices one account can use at once.
- Sign people out automatically after a period of inactivity.
- See who is signed in right now, and end any session with one click.
Control apps, API keys and AI agents
More and more tools reach WordPress without a browser: apps signed in with application passwords, the REST API and AI agents.
- Application passwords. See every key on the site, when it was last used, and revoke it. Switch keys off for the whole site or for chosen roles.
- Confirm risky actions. Ask for the password again before someone installs a plugin, makes a new administrator or creates a new key, so a stolen browser session can’t do it.
- API & Agent Access. One page showing what each plugin exposes: REST routes, public AJAX actions, scheduled tasks and AI agent tools.
- Outbound connections. See which outside servers your plugins contact through WordPress.
AI security for your site
AI agents and AI search bots now read WordPress sites every day. Ultimate Security helps you keep them safe and in check. Every AI feature is off until you turn it on.
- Prompt injection scan. Finds hidden text written to trick AI agents into doing something: instructions hidden from visitors, invisible characters and links built to leak data. It checks posts, custom fields and page-builder content, comments (pending ones too), menus, author profiles, categories, widgets and the site title. Move a matching comment to the Trash or strip the hidden part of a post after a preview, or open the item and edit it yourself. No AI needed, and nothing leaves your site.
- Weekly AI safety scan. Optionally scans every week and emails you about new high-risk finds.
- AI tool check. Flags AI tools from other plugins that can change your site and are offered to every AI agent, or that skip their permission check.
- AI crawler visits. See which AI bots fetch your pages (GPTBot, ChatGPT-User, OAI-SearchBot, ClaudeBot, Claude-SearchBot, PerplexityBot, Amazonbot, CCBot, Bytespider, DuckAssistBot and others), when they last came and what they are for, without Cloudflare. Block them with the Cloudflare firewall rules or robots.txt.
- Connect ChatGPT, Claude and Cursor safely. Let them read your security status through a sign-in you approve once on your site. Read only, and you can disconnect each app at any time.
- Claude, Cursor and VS Code. Share read-only security tools and ready-made prompts (“Run a security review”) with AI apps through the official WordPress MCP Adapter.
- Explain with AI. On WordPress 7 and newer, an “Explain” button on Security Fixes, Security Events and sensitive settings pages asks the AI provider you set up in WordPress for a plain-language answer. Addresses, user names and your login address are removed before anything is sent.
- Ask your AI. Copy a ready-made question about any security issue into ChatGPT, Claude or any AI chat. No AI key needed.
Block spam and bots on your forms
Add Google reCAPTCHA or Cloudflare Turnstile to your login, registration, password reset and comment forms, and to WooCommerce login, registration and checkout.
- Check that your keys work before going live.
- If the CAPTCHA service is down, your forms keep working.
- Won’t clash with another CAPTCHA plugin on the same form.
Find security problems before hackers do
Vulnerability scanner. Checks WordPress, your plugins and your themes against a database of known security holes, and emails you when it finds one. It works without an API key; WPScan or Patchstack keys add extra coverage. Holes that attackers are known to use are marked and listed first.
- Runs on a schedule in the background.
- Flags plugins that haven’t been updated in a long time.
- Results show in the dashboard, Site Health and your plugins list.
Security score. One number that tells you how well protected your site is, which fix to do next, and how it has changed over time.
File check. Compares your WordPress core files with the official copies, so changed or added files stand out.
See what is happening. Security Fixes lists everything that needs attention, most serious first, with fixes you can preview before they run. Security Events shows recent sign-ins, failed sign-ins and lockouts. Troubleshoot checks the things your protections rely on, including whether your server’s PHP has the latest security fixes, and Security Baseline tells you when a setting changes. You get an email when any account gains the power to install plugins, change settings or manage users, or is signed in without the login form. You are also told when a plugin appears or changes unexpectedly, or hides from your Plugins list. If you think someone got in, Emergency Lockdown stops all plugin and theme changes for a set time while you clean up, without taking your site offline. The Application Passwords and API & Agent Access pages show which apps and AI tools can reach your site.
Safer updates. Choose when WordPress, plugins and themes update automatically. Set update days and quiet periods, delay updates by a few days, and get an email when something changes.
Advanced protection
Cloudflare firewall rules. If your site uses Cloudflare, connect your account and turn on ready-made rules from wp-admin: let good bots through, block bad crawlers, AI crawlers and risky traffic, and block attacks on known WordPress flaws before you’ve had a chance to update. You can preview every rule before it goes live. New block rules can start as a challenge for 24 hours, so you see their effect before anyone is blocked.
Security keys (salts). Change the secret keys in wp-config.php on demand or on a schedule, which signs everyone out and makes stolen login cookies useless. You get a warning before a scheduled change, and can restore a previous set.
Test Mode
Turn on your protections without blocking anyone, and review a log of what would have been blocked. Choose which user roles it covers. Visitors who aren’t signed in are still held to the login limit, and Test Mode switches itself off after seven days, so a forgotten test never leaves your site unprotected.
Moving from another plugin
- Import your two-factor and login settings from Wordfence Login Security. Preview it first and undo it if you change your mind.
- Import your login limits and blocked usernames from Wordfence, Solid Security or All In One WP Security, plus the hidden login address from the last two. You see every change first, nothing is weakened, and one click undoes it.
- Copy your settings to another site, or keep a backup, as a file.
- Detects WooCommerce, Ultimate Member, page builders, form, caching and SEO plugins, and warns you if another security plugin is already doing the same job.
Privacy
No usage tracking. The plugin contacts an outside service only when you switch on a feature that needs one, and each is listed under External Services below.
For developers
wp ultimate-security template list
wp ultimate-security template apply <template> [--dry-run]
wp ultimate-security template undo
wp ultimate-security export [--file=<path>]
wp ultimate-security import <file> [--dry-run]
wp ultimate-security status
wp ultimate-security unlock <user> | --ip=<address> | --all
wp ultimate-security 2fa status <user> [--format=json]
wp ultimate-security 2fa disable <user>
wp ultimate-security captcha off
wp ultimate-security login-url reset
wp ultimate-security agent summary | findings | events | actions | plan
wp ultimate-security agent preview <action> [--args=<json>]
AI tools: with “Share security findings with AI agents” on, read-only abilities (security summary, findings, events, vulnerabilities, update status, login protection status, fix previews) and three prompts appear in the WordPress Abilities API, so the official MCP Adapter offers them to AI apps. REST: /wp-json/ultimate-security/v1/agent/* for administrators.
Video guides
- Set up an authenticator app
- Two-factor login by email
- Hide your login page
- Set strong password rules
- Limit login sessions
- Manage plugin and theme updates
- Change your security keys after a breach
- Spot changed WordPress files
- Understand Site Health reports
- Dashboard walkthrough
- Move your Wordfence two-factor settings
Learn more
- Website — features and articles.
- Documentation — setup guides, troubleshooting and how-tos.
- YouTube — all video guides.
External Services
This plugin connects to the following third-party services, and only when you use the related feature:
Google reCAPTCHA
- When: reCAPTCHA protection is enabled. The reCAPTCHA script is then loaded in your visitors’ browsers on the protected forms.
- Data sent: the visitor’s reCAPTCHA response token, your site secret key, and the visitor’s IP address for verification.
- Endpoints: https://www.google.com/recaptcha/api.js (browser script, with a preconnect to https://www.gstatic.com) and https://www.google.com/recaptcha/api/siteverify (server-side verification).
- Terms: https://policies.google.com/terms — Privacy: https://policies.google.com/privacy
Cloudflare Turnstile
- When: Cloudflare Turnstile protection is enabled. The Turnstile script is then loaded in your visitors’ browsers on the protected forms.
- Data sent: the visitor’s Turnstile response token, your site secret key, and the visitor’s IP address for verification.
- Endpoints: https://challenges.cloudflare.com/turnstile/v0/api.js (browser script) and https://challenges.cloudflare.com/turnstile/v0/siteverify (server-side verification).
- Terms: https://www.cloudflare.com/website-terms/ — Privacy: https://www.cloudflare.com/privacypolicy/
WPVulnerability
- When: the Vulnerability Scanner runs. This is the default vulnerability database and requires no API key.
- Data sent: your WordPress version and the slugs of your installed plugins and themes.
- Endpoint: https://www.wpvulnerability.net/
- Privacy: https://www.wpvulnerability.net/
WPScan
- When: the Vulnerability Scanner runs and you have configured a WPScan API key.
- Data sent: your WPScan API key, your WordPress version, and the slugs of your installed plugins and themes.
- Endpoint: https://wpscan.com/api/v3/
- Terms: https://wpscan.com/terms-of-service/ — Privacy: https://wpscan.com/privacy-policy/
Patchstack
- When: the Vulnerability Scanner runs and you have configured a Patchstack API key.
- Data sent: your Patchstack API key, your WordPress version, and the slugs of your installed plugins and themes.
- Endpoint: https://patchstack.com/database/api/v2/
- Terms: https://patchstack.com/terms-of-service/ — Privacy: https://patchstack.com/privacy-policy/
CISA Known Exploited Vulnerabilities
- When: only when a vulnerability scan starts (scheduled or “Scan now”), at most once a week. Your site downloads CISA’s public list of vulnerabilities that attackers are known to use, so those can be marked and listed first.
- Data sent: nothing beyond a normal web request (GET) for that public file from your site’s server. No site data is sent. Only the vulnerability IDs (CVE numbers) are kept.
- Endpoint: https://www.cisa.gov/sites/default/files/feeds/known_exploited_vulnerabilities.json
- Terms: https://www.cisa.gov/known-exploited-vulnerabilities-catalog — Privacy: https://www.cisa.gov/privacy-policy
WordPress.org Plugin and Theme Information API
- When: the Vulnerability Scanner checks whether an extension has been abandoned, and when the Update Manager gathers update information.
- Data sent: the slugs of your installed plugins and themes (no user data).
- Endpoints: https://api.wordpress.org/plugins/info/1.2/ and https://api.wordpress.org/themes/info/1.2/
- Privacy: https://wordpress.org/about/privacy/
WordPress.org Core Version Check
- When: the Update Manager checks for available WordPress core updates.
- Data sent: a standard WordPress core version-check request (no user data).
- Endpoint: https://api.wordpress.org/core/version-check/1.7/
- Privacy: https://wordpress.org/about/privacy/
WordPress.org Core Checksums
- When: you run the WordPress core file-integrity check.
- Data sent: your WordPress version and locale, in order to retrieve the official file checksums for comparison.
- Endpoint: https://api.wordpress.org/core/checksums/1.0/
- Privacy: https://wordpress.org/about/privacy/
WordPress.org Secret-Key (Salt) API
- When: you rotate WordPress security keys and salts, on demand or on a schedule.
- Data sent: a request for …
Screenshots

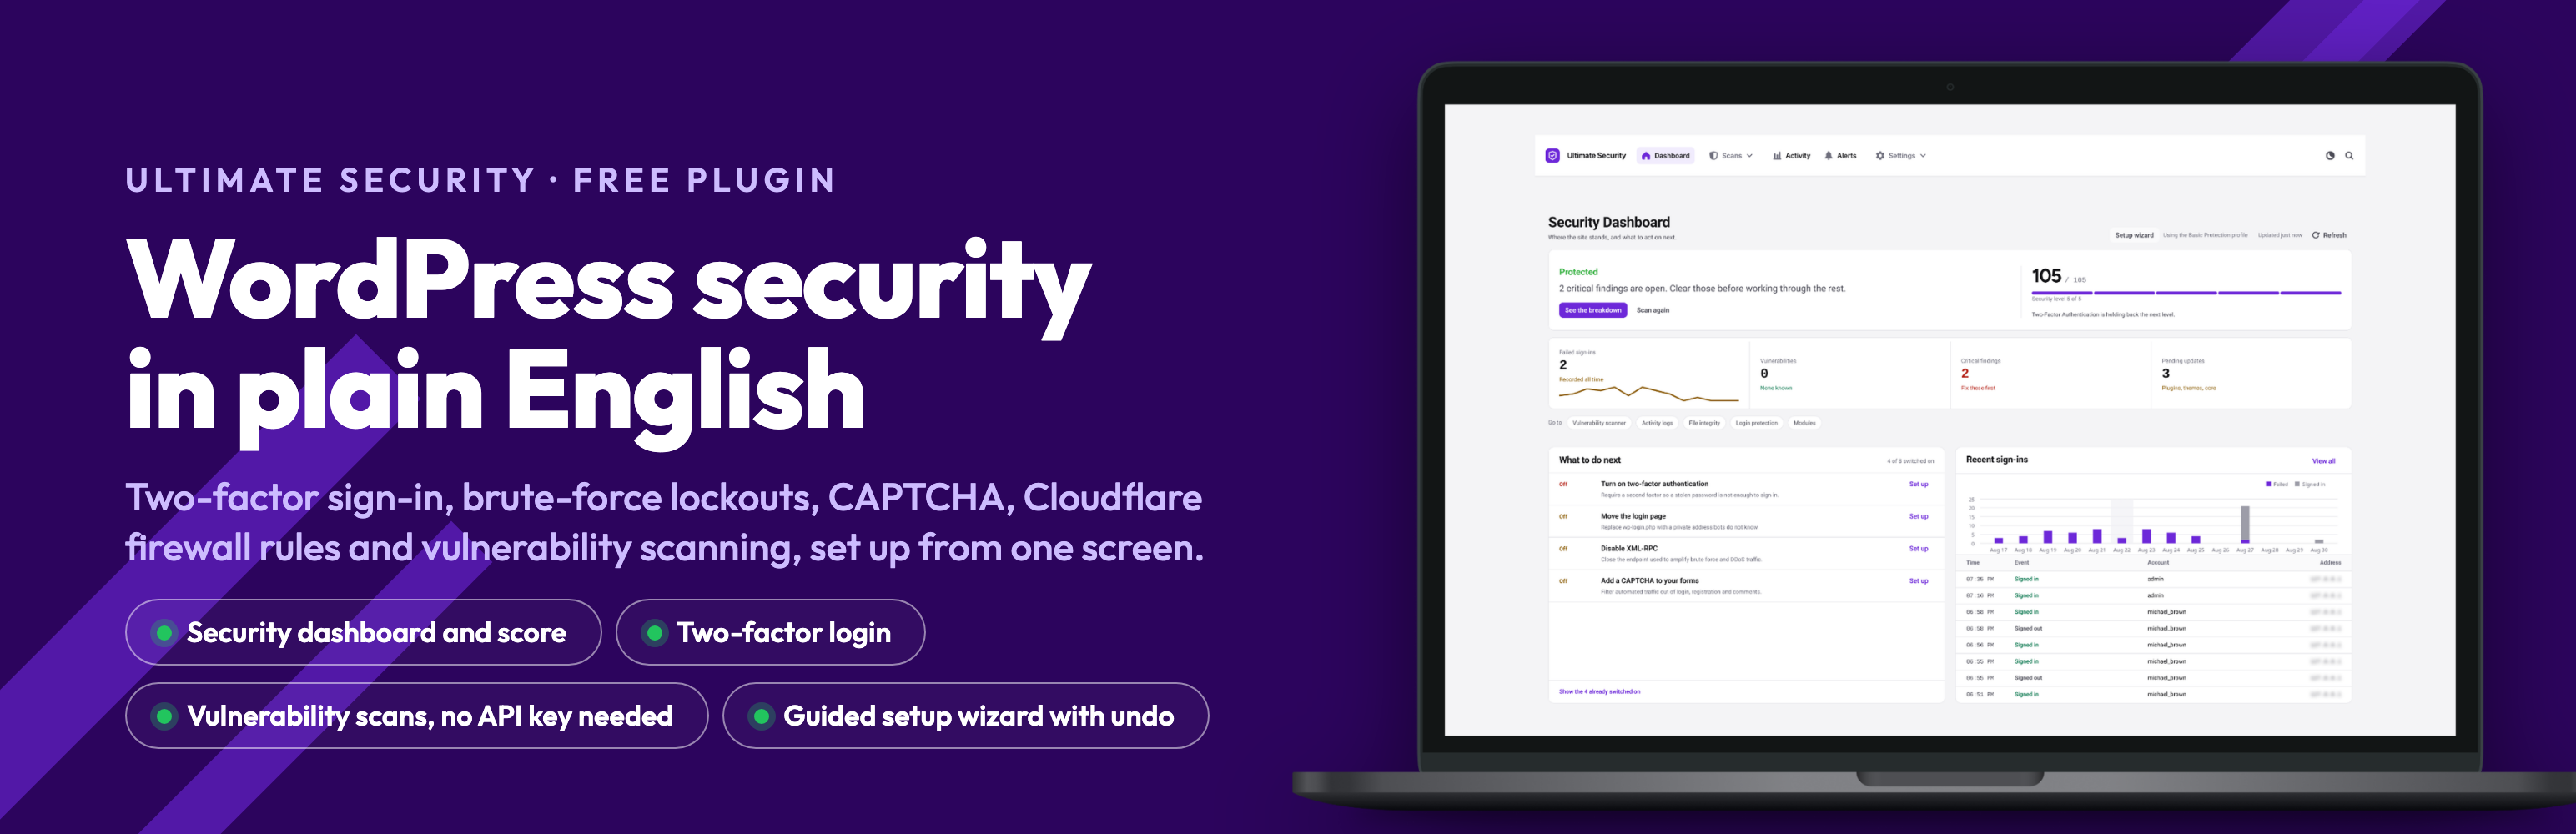
The dashboard tells you in plain words how safe your site is and what to fix next.

Answer a few questions and the setup wizard secures your site. You see every change first and can undo it later.

Stop bots that guess passwords. Repeat offenders are locked out for longer.

Test Mode shows what would have been blocked, without blocking anyone.

Add a second step to login with an email code or an authenticator app.

Hide your login page and require strong passwords.

Stop spam bots on your login, comment and WooCommerce forms with reCAPTCHA or Cloudflare Turnstile.

Find plugins, themes and WordPress versions with known security holes, automatically.

Turn on ready-made Cloudflare firewall rules without writing any code.

See who is signed in right now and sign anyone out with one click.

Switch each feature on or off. Your site stays fast.

Bring your settings over from Wordfence Login Security, or copy them to another site.