Hide your login page. Starve the bots.
Brute-force bots hammer wp-login.php on every WordPress site — thousands of password guesses a day, around the clock. They can only attack a door they can find. The simplest fix is to hide the login page: rename wp-login.php to a custom login URL that only you and your team know.
VanishLogin moves that door. Your login form lives at a custom login URL only you know (like yoursite.com/my-secret-door), while the old wp-login.php stops answering anyone who is logged out. Your access logs go quiet, your server stops wasting resources on bot traffic, and password guessing has nowhere to land.
What it does
- Hide your login page — change wp-login.php to any secret slug, with live validation, a live URL preview, and one-click copy
- Choose what intruders get — logged-out visitors hitting wp-login.php or wp-admin receive a 404, your homepage, or a custom URL of your choice
- Intruder IP log — every hit on the old login page, grouped by IP with hit counts and last-seen times; block or unblock any IP in one click (blocked IPs are refused everywhere, including the secret login URL — and you can never block your own IP)
- Modern settings dashboard — protection status pill, blocked-intruder hit counter, and your full login URL at a glance
- Never get locked out — a one-line emergency bypass in wp-config.php disables protection instantly, and logged-in users are never blocked
- Plays well with others — password reset, logout, registration, and re-auth links keep working; pairs perfectly with 2FA and limit-login-attempts plugins
How it works
- Turn protection on and pick your secret slug.
- Share the new login URL with your team — bookmark it.
- Bots keep knocking on wp-login.php and get a 404. You log in at your secret address like always.
Built like a security tool should be
- Small codebase, no tracking, no telemetry, no upsells — 100% free under the GPL
- Nothing leaves your server; the intruder log is stored in your own database
- Honest about its layer: hiding the login page removes the target, and pairs with 2FA and login-attempt limiting for defense in depth
Built by WordPress security specialist Md Jahid Bin Sabit.
Credits
VanishLogin is designed, built, and maintained by Md Jahid Bin Sabit — WordPress security specialist.
- Website: https://jbsabit.com/
- WordPress.org profile: https://profiles.wordpress.org/jbsabit/
- Contributor: Reflecters — https://profiles.wordpress.org/wearereflecters/
Screenshots
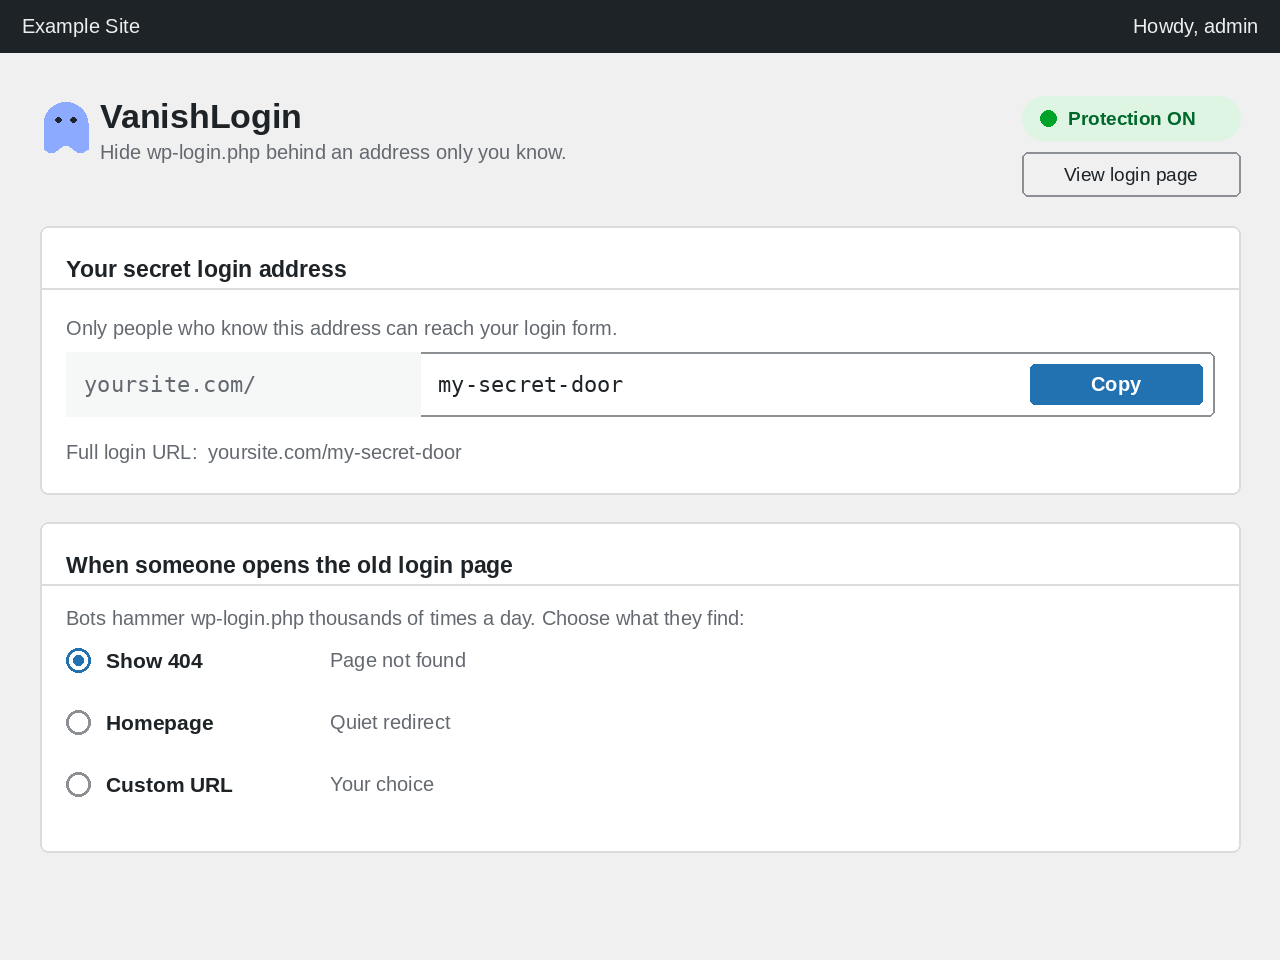
Set your secret login URL and choose what intruders see on the old wp-login.php — a 404, your homepage, or a custom URL.
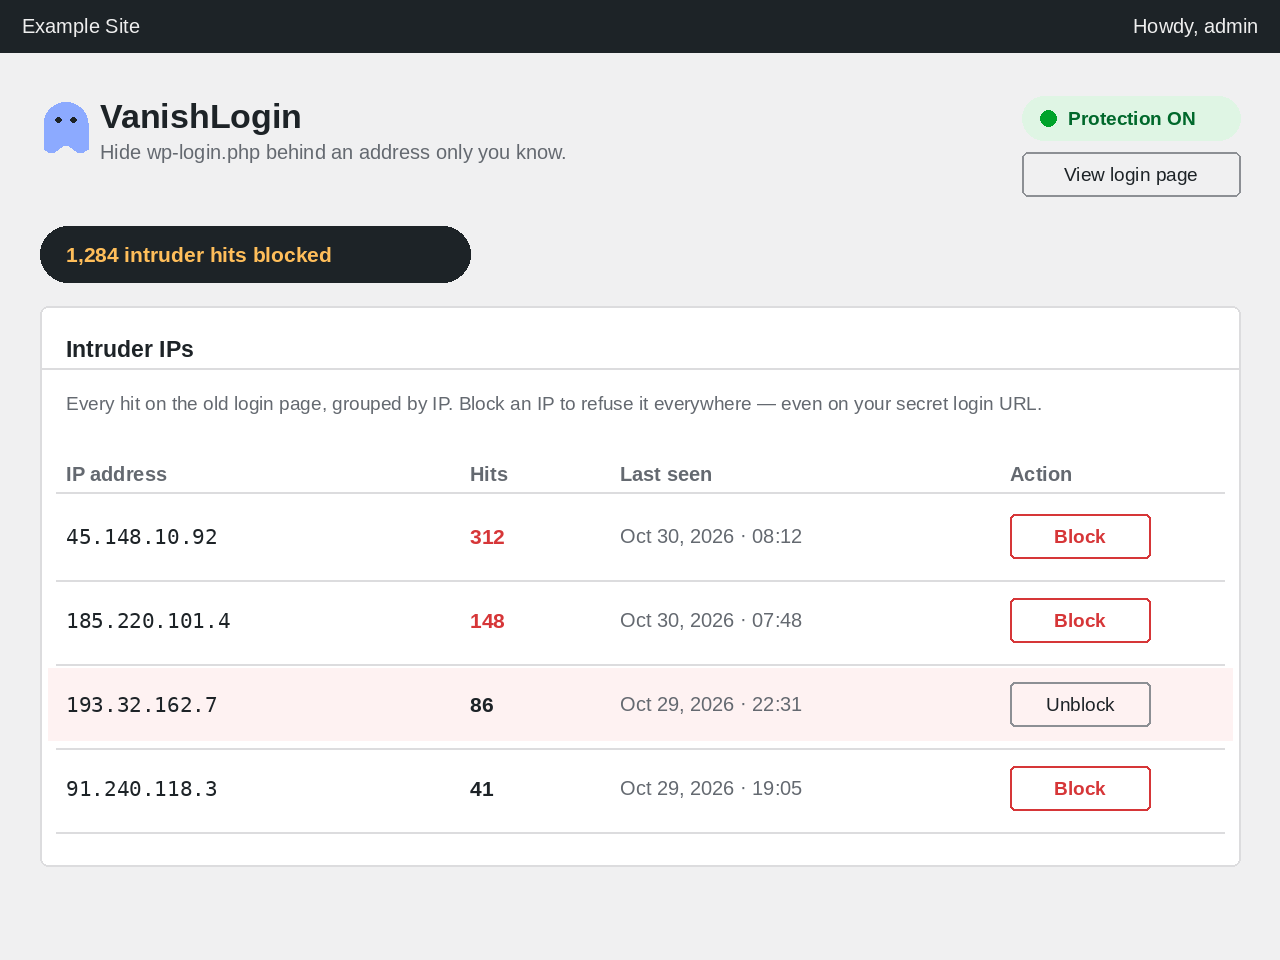
Intruder IP log: every hit on your old login page, grouped by IP with hit counts — block any IP in one click.
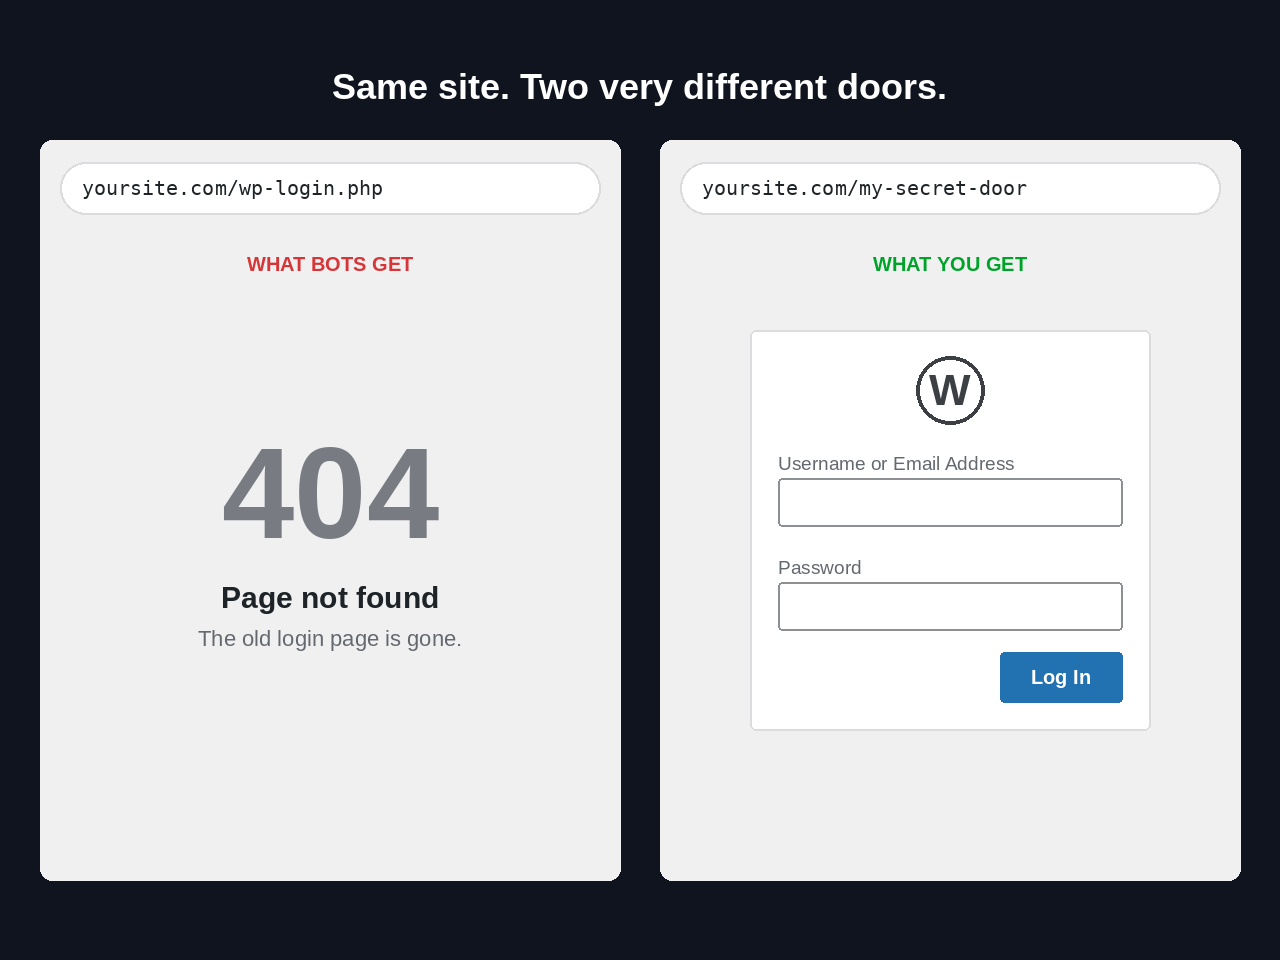
Bots get a 404 on wp-login.php. You get the real login form at your secret address.
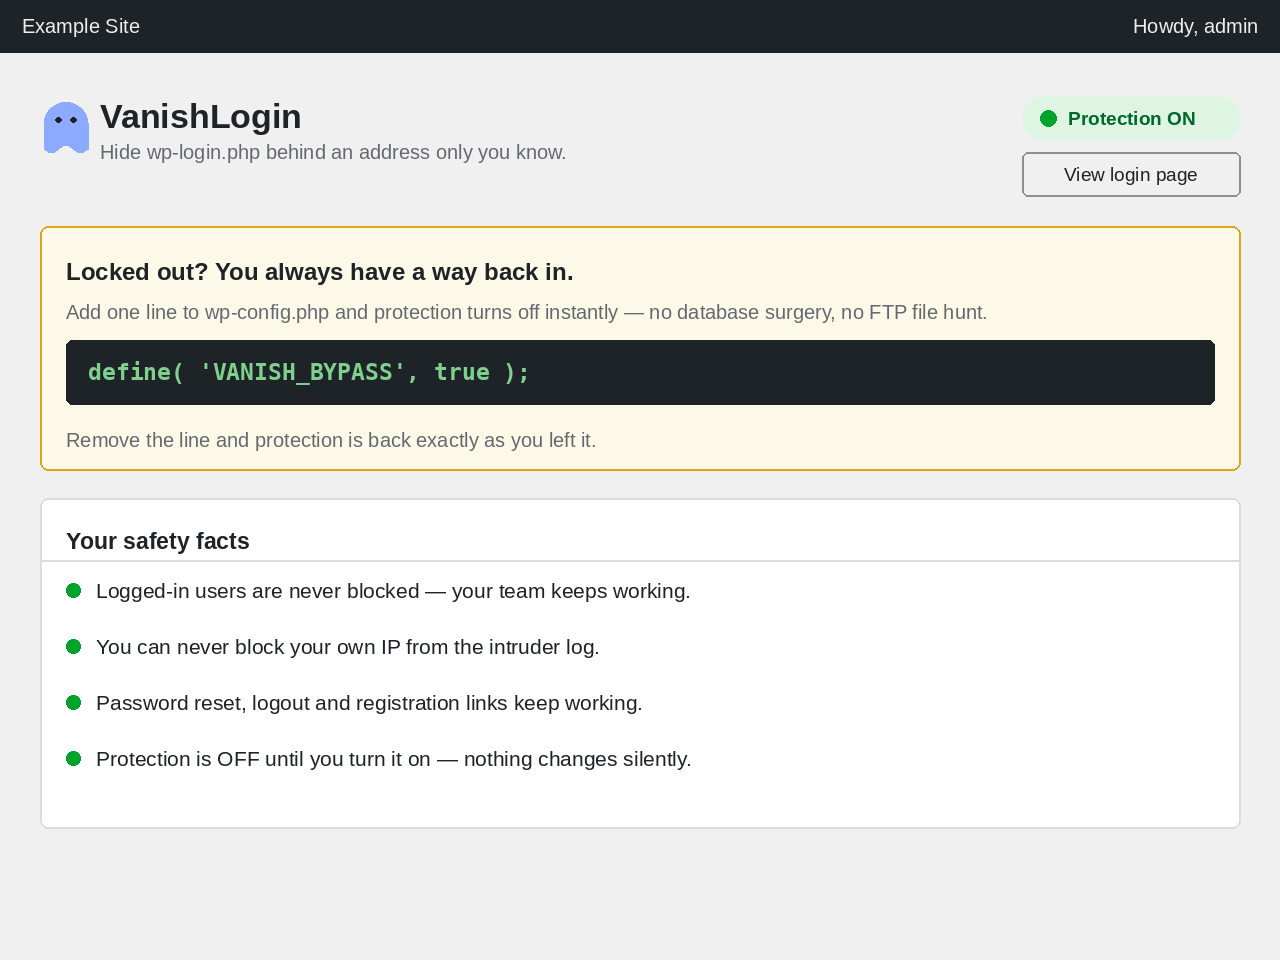
Never lock yourself out: the emergency bypass and your safety facts, always one screen away.